NetScaler MPX 9200 FIPS
Welcome to the next-generation NetScaler MPX 9200 FIPS platform. This section provides comprehensive instructions on how to deploy your appliance efficiently and configure it for optimal performance.
The MPX 9200 FIPS is a 1U FIPS 140-3 Level 2 application delivery platform. It represents the latest advancement in NetScaler technology, featuring enhanced processing power, improved connectivity options, and robust management capabilities.
Note:
For certification information and FIPS-specific software information, see MPX FIPS appliances.
Key specifications
-
Processor: Intel Xeon 5th-generation processor architecture
-
Memory: 128 GB DDR5 ECC RDIMM memory for enhanced performance
-
Data ports: Dual 4 x 50G high-speed ports with PCIe 4.0 support
-
Power: Redundant CRPS power supplies for high availability
-
Management: Dedicated BMC with IPMI 2.0 and Redfish for full out-of-band control
-
Security: FIPS 140-3 Level 2 compliance with tamper-evident seals on the chassis
Prepare for installation
Carefully inspect your shipment to ensure that all components are present and undamaged. The following items are included with your NetScaler 1U appliance:
Before installing your new appliance, carefully unpack the unit and verify that all the components are present. The only tools required for installing the appliance are a Phillips screwdriver, a flathead screwdriver, and a cage nut insertion tool (if installing into square-hole racks). Your NetScaler 1U package should include the following items:
Hardware components:
- 1x NetScaler MPX 9200 FIPS appliance, with the front ear and handle assemblies pre-installed on the chassis
- 1x standard 4-post rail kit (19-inch rack compatible), which includes:
- Left rail (x1)
- Right rail (x1)
- Mounting screw kit (includes M4x4L, M4x6L, and M5x20L screws)
The included accessory kit contains essential connectivity hardware, including two power cords to support redundant power supply operation.
Notes:
Rail kit compatibility varies by rack manufacturer and configuration. If the provided rail kit does not fit your specific rack infrastructure, contact your NetScaler sales representative immediately to obtain an appropriate alternative mounting solution.
Before proceeding, examine all components for shipping damage. Report any damaged items to your carrier and NetScaler support before beginning the installation process.
Infrastructure requirements
-
Compatible 19-inch rack with adequate depth clearance (minimum 550 mm)
-
Proper airflow management with front-to-rear cooling path
-
Available rack units (1U height requirement)
-
Adequate weight support (system weight: 25.2 lbs)
Network infrastructure:
-
Administrative LAN with available switch ports
-
Dedicated out-of-band management network
-
Appropriate network cables (Cat5e/Cat6 for management, fiber/DAC for data)
-
A 50 GbE capable switch for the SFP56 data ports
Power requirements:
- Dual power sources (recommended for redundancy)
- Frequency operating range: 47 Hz – 63 Hz
- Adequate power capacity (full load 110 V: 406 W/240 V: 394.57 W)
- PSU input connector: IEC320-C14 (Male)
- Required power cord: IEC320-C13 to NEMA 5-15P (or regional equivalent)
- Rating: Minimum 10 A / 250 V
Detailed AC input voltage specifications:
| Voltage Range | Minimum | Rated Operating Range | Maximum | Brown Out | Brown In |
|---|---|---|---|---|---|
| 115 V Range | 90 Vrms | 100-127 Vrms | 140 Vrms | 75 Vac+/-4 V | 85 Vac+/-4 V |
| 230 V Range | 180 Vrms | 200-240 Vrms | 264 Vrms | N/A | N/A |
Maximum input current requirements:
| Input Voltage Range | Maximum Current |
|---|---|
| 100 Vac – 127 Vac | 10 A |
| 200 Vac – 240 Vac | 5 A |
| 240 Vdc | 5 A |
Management station requirements
-
Workstation or laptop (Windows or macOS) with network connectivity
-
Web browser with JavaScript and HTML5 support (Chrome, Firefox, Safari, or Edge)
-
Terminal emulator software for CLI access
-
Administrative privileges for network configuration
Hardware platform
The MPX 9200 FIPS integrates management, console, and high-speed data interfaces on the front panel, and power, cooling, and identification components on the rear panel. Identify each component before you cable the appliance.
Front panel components
The front panel groups the console and management ports, the storage bay, the data ports, and the FIPS tamper seals.
The following figure shows the front panel of the MPX 9200 FIPS appliance.
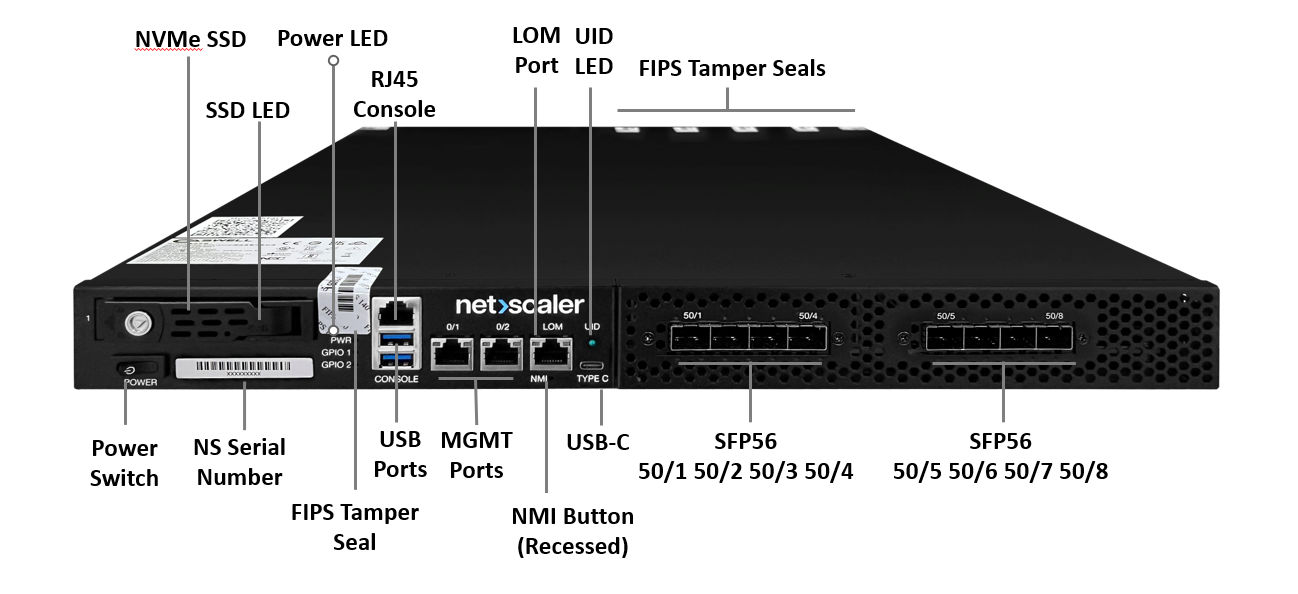
| Label | Component Type | Technical Specification | Primary Function |
|---|---|---|---|
| CONSOLE | RJ-45 console port | RS-232 compatible, 9600-8N1 | Direct serial console for initial CLI access |
| MGMT 0/1 & 0/2 | Dual Ethernet ports (1000Base-T) | 1000Base-T, auto-negotiate | Primary and secondary in-band management |
| LOM | Dedicated IPMI port | IPMI 2.0/Redfish | Out-of-band hardware monitoring and control |
| NMI | Recessed pinhole button | Non-maskable interrupt | Force kernel core dump for crash analysis |
| PWR | Soft-push button (4-second on/off) | Power management | Power on and graceful shutdown control |
| USB | Two USB Type-A ports (optional) | USB | Service and recovery use |
| TYPE-C | USB Type-C console port (optional) | Alternate console | Secondary console and debug interface |
| UID | Locator LED | Blue LED indicator | Visual system identification in the rack |
| GPIO1/GPIO2 | User-defined GPIOs | General-purpose I/O | Not used; disabled by default on the 1U platform |
| 50/1–50/8 | SFP56 data ports | Two 4-port SFP56 NICs | 50GbE data interfaces; PCIe 4.0 x16 |
| FIPS Seal | Tamper-evident label | FIPS 140-3 Level 2 | Tamper evidence across the front of the top cover |
Rear panel components
The rear panel houses dual CRPS power supplies, the cooling fans, the rear UID LED, the PSU alarm-mute button, and the rear power button.
The following figure shows the back panel of the MPX 9200 FIPS appliance.
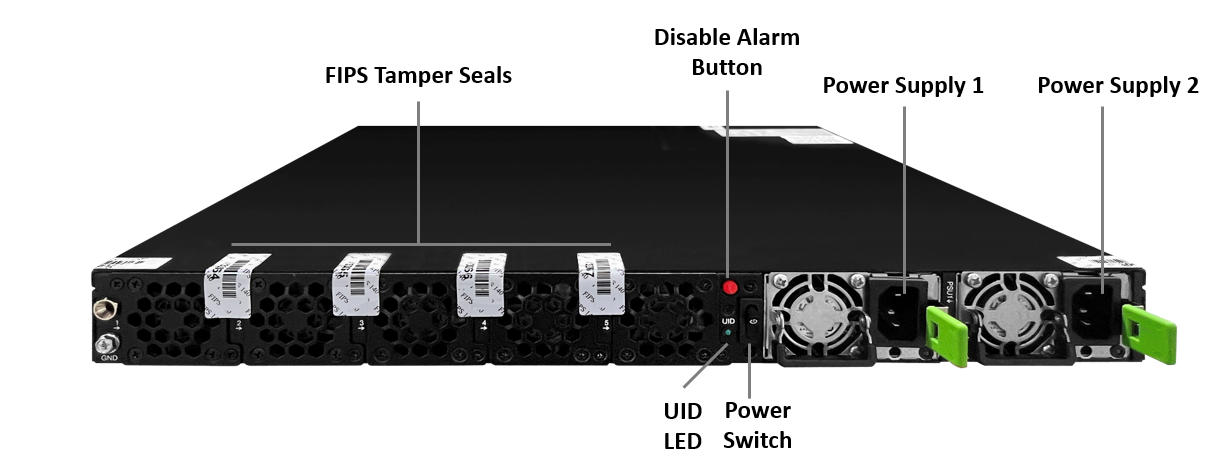
| Component | Technical Details | Operational Characteristics | Service Information |
|---|---|---|---|
| PSU1/PSU2 | CRPS PSU, up to 800 W each | Redundant N+1 configuration | Hot-swappable during operation |
| Rear UID LED | Blue LED locator | Blue LED indicator | Remote chassis identification |
| PSU Alarm Mute | Red push-button | Silences the audible alarm on PSU fault or loss of AC input | Press once to acknowledge the PSU alarm |
| Rear Power Button | Soft-push, optional | Mirrors the front-panel power button function | Dual power control access |
| Fan Modules | 5 system fans | Smart fan control managed by the BMC | No field replaceable Fan FRU |
| FIPS Seals | Tamper-evident labels | FIPS 140-3 Level 2 | Across the top cover, spanning fans 1–5 |
Note:
FIPS 140-3 Level 2 tamper evidence. Tamper-evident seals are applied across the top cover at the front and rear of the chassis (spanning fans 1–5). The seals form the physical security boundary. Inspect them on receipt and periodically during operation. If any seal is cut, lifted, or missing, treat the unit as potentially compromised and contact NetScaler Support. Confirm the seal count and placement against the platform Security Policy.
Install the hardware
Rack-mount the appliance
Install the appliance into a 19-inch rack in four stages: attach the inner rails, install the outer rails, mount the appliance, and secure it to the rack. The left and right rails are symmetrical. Repeat each rail step on both sides.
Note:
The front ears are pre-installed. The modified handle is set inward from the mounting flange, exposing the M5 rack-mount hole in the ear. The ear and handle assemblies are shipped pre-installed on the chassis, and the packing foam is shaped to hold them in place. You do not attach the ears during installation. Do not remove them.
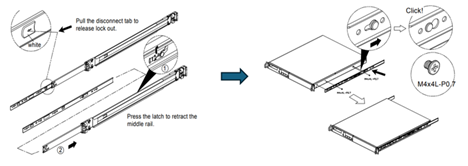
Attach the inner slide rails
-
Pull the white disconnect tab to release and detach the inner rail member from each slide rail.
-
With the stamped text facing outward, align the inner rail with the chassis mount points, using the black reference markers on both sides of the chassis.
-
Slide the rail toward the rear until it clicks firmly into the locked position.
-
Fasten each inner rail using the provided M4x4L screws, as shown in the diagram.
-
Repeat this process for both the left and right sides of the chassis.
Install the outer slide rails
- Hold the outer rail assembly against the rack frame.
- Align the mounting brackets with the rack post holes at the selected U-height.
- Insert the rail mounting mechanism into the rack posts until it engages.
- Listen for an audible “click” to confirm that the rail is properly seated and locked.
- Ensure both the front and rear mounting points are securely attached to the posts.
- Verify that the rails are level and parallel using the numbered rack post markings.
- Repeat this process for both the left and right outer rail assemblies.
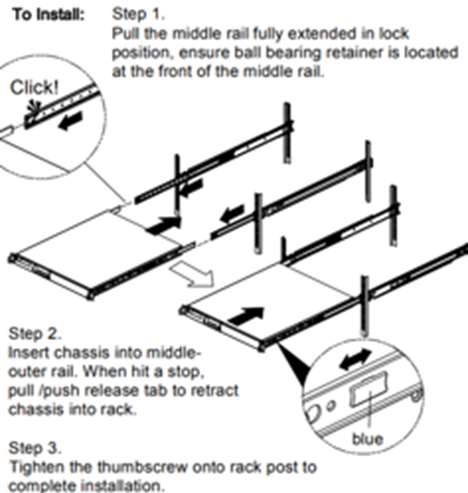
Mount the unit onto the rails
- Carefully align the chassis-mounted inner rails with the rack-mounted outer rails.
- Smoothly slide the system into the rack until the locking mechanism engages.
- If necessary, apply light, even pressure to ensure the unit locks securely into place.
Step 4: Secure the appliance to the rack
- Slide the appliance fully into the rack until the front ears are flush against the rack posts.
- Align the mounting holes in the front ears with the corresponding holes in the rack posts.
- Insert a standard M5 rack screw through each ear and into the rack post.
- Tighten the screws evenly to secure the appliance to the rack. Do not overtighten.
Note: Front ears secured to the rack posts. The red arrows mark the M5 rack-mount holes on the left and right ears.
- Verify that the appliance is level and securely fastened to the rack.
Safety considerations
For safety and equipment durability, ensure that the following requirements are met:
-
Maintain a minimum of 2 inches of clearance at the front and rear of the chassis to ensure proper ventilation.
-
Verify the rack’s weight capacity before installation and ensure that the rack is stable and properly secured to the floor.
-
Use proper lifting techniques. The system weight is approximately 25.2 lbs.
-
Strictly follow electrical safety procedures when connecting the appliance to a power source.
Note:
The MPX-9200-FIPS 1U platform requires unobstructed front-to-rear airflow for optimal cooling. Restricted airflow results in overheating and trigger system protection mechanisms.
Network and power connections
Connection sequence
Follow this specific connection order to ensure proper system initialization and to avoid configuration conflicts.
-
Management network connectivity
-
Connect the MGMT 0/1 port to your administrative LAN, using Cat5e/Cat6.
-
Verify that the network switch port configuration supports auto-negotiation.
-
Confirm network connectivity and VLAN configuration, if applicable.
-
Document the assigned IP address and network parameters.
-
-
Out-of-band management setup
-
Connect the LOM port to a dedicated OOB management network.
-
Use network infrastructure that is separate from production traffic.
-
Leave the LOM port in dedicated mode operation (factory default).
-
-
Data port configuration
-
Install SFP56 (or compatible SFP28/SFP+) transceiver modules in data ports 50/1–50/8.
-
Match each transceiver type to the switch port capability. Use NetScaler-qualified transceiver MPNs for guaranteed interoperability.
-
Connect the fiber or DAC cables to the data ports as required.
-
Confirm that the cable rating matches the 50GbE port speed.
-
-
Power system connection
-
Connect the first power cord to the PSU1 input receptacle.
-
Connect the second power cord to the PSU2 input receptacle.
-
Use independent AC feeds where possible for N+1 redundancy.
-
Verify that the input voltage is 100–240 VAC, 50–60 Hz, before applying power.
-
-
System startup
-
Press the front-panel PWR button to initiate the boot sequence.
-
Observe the front-panel LEDs. The PWR LED must illuminate solid green.
-
Verify that both PSU LEDs are solid green within 10 seconds of power-on.
-
Allow the full boot cycle to complete (about 4–5 minutes) before accessing the system.
-
Note:
Use NetScaler-qualified transceiver and cable part numbers for guaranteed interoperability and support coverage.
Power supply status indicators
The CRPS power supplies provide comprehensive status information through integrated LED indicators located on each power supply faceplate.
| LED Indicator | PSU State | System Impact | Action Required |
|---|---|---|---|
| Solid GREEN | AC present, all DC rails active under load | Normal operation | None - normal |
| 1 Hz Blink GREEN | AC present, 12 Vsb active including 5 Vsb for BMC power, main rails idle | Redundant standby (N+1) | None - normal |
| Solid AMBER | AC input lost or disconnected | Lost redundancy (if N+1) or system down | Check the AC power connection |
| 1 Hz Blink AMBER | OCP/OVP/OTP warning threshold reached | Degraded PSU operation/potential shutdown | Verify PSU cooling and airflow |
| Solid AMBER | Critical fault (OCP/OVP/OTP tripped) | PSU shutdown for protection | Replace the PSU immediately |
System access and configuration
Configure the appliance through the NetScaler GUI or the CLI. Both methods provide full access to the initial setup. Use the default addresses and credentials below for first access, and then change them during setup.
| Interface or Service | Default User Login Credentials | Default IP Address | Subnet Mask or Gateway | Description or Note |
|---|---|---|---|---|
| NSIP (MGMT 0/1) | nsroot or product SN | 192.168.100.1 | 255.255.0.0/16 | Default NetScaler IP for initial configuration |
| LOM/IPMI Port | nsroot or product SN | 192.168.1.3 | 255.255.255.0/24 | Out-of-band management IPMI, Redfish, remote iKVM, power control |
Note:
The default password is the device serial number. Enter it exactly as printed on the chassis label. All credentials are case-sensitive. Change the default password during the initial setup.
Console connection setup by using the GUI
The web management interface provides complete configuration through a browser. The appliance is managed through the MGMT 0/1 port at the default NSIP.
-
Network preparation
-
Connect the management workstation to the MGMT 0/1 port or to the same VLAN.
-
Set a static IP on the workstation in the 192.168.100.X/16 range (for example, 192.168.100.50).
-
Verify network connectivity by performing a ping test to the default NSIP address: 192.168.100.1.
-
Ensure that firewall settings allow HTTPS traffic (TCP 443).
-
-
Browser configuration
-
Open a Web browser (Chrome, Firefox, Safari, or Edge).
-
Enter
https://192.168.100.1. -
Accept the self-signed certificate warning to continue.
-
-
Initial authentication
-
In the Username field, enter
nsroot. -
In the Password field, enter the device serial number exactly as printed on the chassis label.
-
Click Login. The system redirects to the initial setup wizard.
-
-
Complete the setup wizard
The setup wizard guides you through the following essential configuration parameters:
-
Management Service IP (NSIP): Assign a static IP for management access.
-
Subnet mask and default gateway: Configure these for your network segment.
-
DNS server: Enter the primary DNS IP address.
-
Hostname: Assign a meaningful system identifier.
-
Administrative password: Set a strong password to replace the serial number default.
-
Console connection setup by using the CLI
The command-line interface provides direct system access for advanced configuration and troubleshooting through the front-panel console port.
-
Physical connection
-
Connect an RJ-45 serial cable to the CONSOLE port on the front panel.
-
Connect the other end to the workstation serial port or to a USB-to-serial adapter.
-
-
Terminal emulator configuration
Open your terminal emulation software (such as PuTTY, Tera Term, or SecureCRT) and configure the following settings:
Setting Value Baud Rate 9600 bps Data Bits 8 Parity None Stop Bits 1 Flow Control None (disabled) Terminal Type ANSI PuTTY Keypad Mode VT100 -
Session establishment
-
Open the terminal emulator application.
-
Establish a connection, using the configured settings.
-
Press Enter if no prompt appears.
-
Wait for the login prompt to display.
-
Authentication process
-
At the login prompt, enter
nsroot. -
At the password prompt, enter the device serial number.
On successful authentication, the system displays the NetScaler command prompt. All credentials are case-sensitive.
-
-
Verify the software and platform identity
After you log in, run
show versionandshow hardwareto confirm the firmware build and the platform identity before you configure the appliance. The following example shows the expected output for the first GA release of the MPX 9200 FIPS.> show version NetScaler NS14.1: Build 43.142.fips.nc, Date: May 22 2026, 20:07:37 (64-bit) (NS14.1-FIPS) Done > show hardware Platform: NSMPX-9200-FIPS-Z 20*CPU+128GB+8*MLX(50)+2*E1K+2*RAPIDS 36010 Manufactured on: 12/19/2025 CPU: 2200MHZ Host Id: 161644678 Serial no: 749FWDTM6K Encoded serial no: 749FWDTM6K Netscaler UUID: 14e3330a-e709-11f0-a8ec-08357136584d BMC Revision: 4.01 Done <!--NeedCopy-->Confirm the following two items in this output:
- The build string ends in
.fipsand the release tag reads(NS14.1-FIPS). Both confirm that the FIPS firmware is running. - The Platform line reports the model descriptor and the platform system ID:
36010, which uniquely identifies the MPX 9200 FIPS.
- The build string ends in
MPX configuration examples
Run the following commands from the NetScaler CLI to establish basic connectivity.
Basic network configuration:
# Configure the NetScaler IP address and subnet mask
set ns config -ipaddress 10.0.0.10 -netmask 255.255.255.0

# Add a subnet IP address for client communication
add ns ip 10.0.0.11 255.255.255.0 -type snip

# Configure the default route for external connectivity
add route 0.0.0.0 0.0.0.0 10.0.0.1

# Configure the system hostname
set ns hostname NS9200-1

# Change the administrative password for security
set system user nsroot -password <yourpassword>
Enter password: *****
Confirm password: *****

# Save the configuration to persistent storage
save ns config

# Restart the system to apply changes
reboot
<!--NeedCopy-->
Note:
Changing the NSIP and rebooting interrupts management connectivity. Reconnect at the new NSIP after the appliance restarts. Always run
save ns configbefore you reboot.
Basic verification commands:
# Check the system software version
show version

# Check the system hardware information
show hardware

# Display the current IP configuration
show ip

# Show the status of all network interfaces
show interface

# Display the routing table
show route

# Verify the configuration save status
show config
<!--NeedCopy-->
LOM port management
Initial LOM configuration
The Lights Out Management (LOM) port provides critical out-of-band access for system monitoring and remote management, independent of the main software operation. Configure the LOM through the web GUI (Method 1) or the CLI with ipmitool (Method 2).
Method 1: LOM web GUI
-
Initial network connection
-
Set a static IP on the management workstation: 192.168.1.10/255.255.255.0.
-
Connect directly to the LOM port using a crossover cable, or connect both to the same switch.
-
Open a browser and navigate to
https://192.168.1.3. The LOM login page appears.
-
-
Default authentication
-
In the Username field, enter
nsroot. -
In the Password field, enter the device serial number (case-sensitive).
-
On the first login, the system forces a LOM password change before granting access.
-
-
Change the default password
-
Enter the current password (device serial number).
-
Enter a new password that meets the complexity requirements shown on the LOM login page.
-
Confirm the new password and click Submit. The system logs out automatically. Log in again with the new password.
-
-
Configure the LOM network
-
Navigate to Settings > Network IP Settings.
-
Select the LAN interface (Default:
eth0). -
IPv4 address configuration: Enter the desired LOM IPv4 address.
-
Subnet mask definition: Set the appropriate subnet mask.
-
Gateway configuration: Enter the default gateway IP address for routing.
-
Click Save to apply.
-
-
Validate connectivity
-
Verify that the new configuration takes effect.
-
Test connectivity by performing a ping test from the management workstation.
-
Attempt to log in using the new IP address to confirm accessibility.
-
Document the final LOM configuration for operational procedures.
-
Note:
Insufficient privilege due to system lockdown. If the LOM GUI shows “Insufficient Privilege (code 8000)” or “You do not have permission to view this content”, System Lockdown is enabled. While lockdown is active, all out-of-band interfaces (LOM web UI, IPMI, and Redfish) are read-only. You cannot change Network Settings, User Management, or other LOM settings until lockdown is disabled. See System lockdown mode.
Method 2: LOM CLI initial configuration (ipmitool)
Access the NetScaler shell through the console, and then use ipmitool to configure the LOM. If System Lockdown is enabled, disable it first.
System lockdown mode
When system lockdown is enabled in-band from the host OS, the BMC enforces out-of-band configuration protection. All platform configuration interfaces, including LOM firmware update, network settings, user management, FRU data, and general LOM configuration, are restricted to read-only access through the LOM web UI and IPMI/Redfish interfaces. No persistent configuration or firmware changes can be performed while lockdown is active.
# Check the system lockdown mode status (return 00 = disabled, 01 = enabled)
ipmitool raw 0x34 0x81

# Unlock or disable system lockdown mode (allow OOB write access based on user privilege)
ipmitool raw 0x34 0x81 0x0

# Lock or enable system lockdown mode (restrict OOB to read-only mode)
ipmitool raw 0x34 0x81 0x1
<!--NeedCopy-->
Configure a static LOM IP address:
# Set LOM to use static IP addressing
ipmitool lan set 1 ipsrc static

# Configure the static IP address
ipmitool lan set 1 ipaddr <new_LOM_IP_address>

# Set the subnet mask
ipmitool lan set 1 netmask <new_netmask_IP_address>

# Configure the default gateway
ipmitool lan set 1 defgw ipaddr <new_gateway_IP_address>

# Cold reboot the BMC (Baseboard Management Controller)
ipmitool mc reset cold
<!--NeedCopy-->
Restore the BMC to factory defaults:
# Restore the BMC to factory default configuration
ipmitool raw 0x32 0x66
<!--NeedCopy-->
Note:
If the IPMI or Network Preserve Configuration option is not enabled in the Maintenance section of the LOM GUI, this operation resets all settings, including LOM network configuration, user accounts, and IPMI web settings, to LOM factory defaults.
Allow approximately 120 seconds for the BMC reboot and network initialization. Test connectivity by performing a ping test after the 120-second initialization period, and verify LOM accessibility using the new IP address before proceeding.
Verify the LOM configuration:
# Display the current LOM network configuration
ipmitool lan print 1

# Test LOM connectivity from an external system
ping <new_LOM_IP_address>
<!--NeedCopy-->
Manage the LOM password from the host. For enhanced security, change the LOM password from the NetScaler shell.
# List the current LOM users to identify the user ID
ipmitool user list 1

# Change the password for a specific user ID (typically user ID 2 for the nsroot admin)
ipmitool user set password <user_ID> <new_LOM_password>
<!--NeedCopy-->
LOM security considerations:
- Change the default password immediately after initial access.
- Implement network-level access controls for the LOM segment.
- Place the LOM on an isolated management VLAN for enhanced security.
- Enable audit logging for administrative actions.
- Re-enable System Lockdown after configuration to protect the OOB interfaces.
Remote power control operations
The LOM interface provides comprehensive remote power management capabilities, enabling administrators to control system power states without physical access to the appliance.
System startup procedure:
-
Pre-startup verification
-
Confirm that both PSU LEDs show solid or blinking green.
-
Verify that the network infrastructure is available.
-
Check for existing hardware alerts in the LOM event log.
-
-
Remote power-on execution
-
Navigate to the Power Control menu in the LOM web UI.
-
Select Power On and click Perform Action.
-
Monitor the front-panel PWR LED for solid green confirmation.
-
-
Startup monitoring
-
Watch for POST completion in the LOM remote console.
-
Confirm that the network interfaces initialize (the MGMT 0/1 interface is accessible at 192.168.100.1).
-
System shutdown procedure:
-
Initiate shutdown
-
Verify that no critical operations are in progress before shutting down.
-
Navigate to Power Control, select ACPI Shutdown, and click Perform Action.
-
-
Confirm verification
-
Monitor the front-panel PWR LED. It extinguishes when the power-off is complete.
-
Wait for full power-off before initiating a subsequent power-on sequence.
-
Note:
Always use ACPI Shutdown for a graceful OS-level shutdown. Use Power Off (immediate) only when the system is unresponsive. Document all remote power events for audit and troubleshooting purposes.
System specifications
Hardware configuration
The MPX 9200 FIPS platform incorporates enterprise-grade components designed for high-performance application delivery and reliability.
Core system architecture
| Component Category | Specification Details | Performance Characteristics |
|---|---|---|
| Regulatory Model | 1U3P3A | FCC and international compliance designation |
| Processor Architecture | Intel Xeon 5th-generation processor | 1 socket, 20 active cores at 2.2 GHz |
| Platform Chipset | Intel C741 PCH | Advanced platform controller hub |
| BMC Controller | Baseboard Management Controller with IPMI 2.0 | Remote KVM, hardware monitoring, power control |
| System Memory | 128 GB DDR5 ECC RDIMM | 2x 64 GB modules, error correction enabled |
| Primary Storage | 800 GB NVMe U.2/U.3 | 2.5-inch high-performance SSD |
| Management Connectivity | Two 1GbE RJ45 (1000Base-T) | MGMT 0/1 (primary), MGMT 0/2 (secondary) |
| Data Connectivity | Two 4-port SFP56 NICs | Ports 50/1–50/8, PCIe 4.0 x16 interface, 8 total 50GbE ports |
Power and environmental specifications
| Parameter | Specification | Operating Range | Notes |
|---|---|---|---|
| Power Supply Configuration | 2x CRPS PSUs, up to 800 W each | Redundant N+1 operation | N+1 redundant, hot-swappable |
| Input Voltage Range | 100–240 VAC | Universal input compatibility | Auto-sensing |
| Input Frequency | 50–60 Hz | Standard utility frequency | ±3 Hz tolerance |
| Input Current | 100-127 V: 10.0 A; 200-240 V: 5.0 A | Variable by input voltage | Maximum ratings |
| Typical System Power Consumption | 300 W | Normal operational load | Steady-state operation |
| Maximum System Power Consumption | 406 W | Peak system utilization | Peak load with both PSUs active |
Environmental specifications
| Environment Factor | Operating Range | Storage Range | Critical Limits |
|---|---|---|---|
| Ambient Temperature | 0-45°C (32-113°F) | -40-70°C | 50°C absolute maximum |
| Relative Humidity | 10-90% RH | 10-95% RH | Non-condensing |
| Operating Altitude | 0-5,000 m | 0-15,200 m | Derated above 8,000 m |
| Typical System Airflow (front-to-back) | ~80.3 CFM | N/A | Full load at nominal 25°C ambient |
| Maximum System Airflow (front-to-back) | ~104 CFM | N/A | Full load at elevated temperature |
Physical specifications
| Dimension | Measurement | Standard Compliance |
|---|---|---|
| Width | 443 mm (17.4”) | EIA 310-D 19-inch rack |
| Depth | 550 mm (21.7”) | Standard server depth |
| Height | 44 mm (1.73”) | 1U rack unit |
| System Weight | 25.6 lbs (11.6 kg) | Approximate operational weight |
| Package Weight | 41 lbs (18.6 kg) | Shipping configuration |
System LED status
The system provides comprehensive status indication through various LED indicators located on the front and rear panels.
Front panel LED status
| LED Indicator | Normal Operation | Fault Condition | Description |
|---|---|---|---|
| PWR (Power) | Solid Green | Off | System power and initialization status |
| UID | Off/blue when set | N/A | Unit locator. Lit on demand through the LOM web GUI |
| GPIO1 | Off (default) | N/A | User-defined function (disabled) |
| GPIO2 | Off (default) | N/A | User-defined function (disabled) |
Power supply LED status
| LED Indicator | PSU State | System Impact | Action Required |
|---|---|---|---|
| Solid GREEN | AC present, all DC rails active under load | Normal operation | None - normal |
| 1 Hz Blink GREEN | AC present, 12 Vsb active including 5 Vsb for BMC power, main rails idle | Redundant standby (N+1) | None - normal |
| Solid AMBER | AC input lost or disconnected | Lost redundancy (if N+1) or system down | Check the AC power connection |
| 1 Hz Blink AMBER | OCP/OVP/OTP warning threshold reached | Degraded PSU operation/potential shutdown | Verify PSU cooling and airflow |
| Solid AMBER | Critical fault (OCP/OVP/OTP tripped) | PSU shutdown for protection | Replace the PSU immediately |
NVMe storage LED status
Each NVMe drive carrier has an activity LED indicator.
| Condition | LED Behavior |
|---|---|
| Idle | LED Off |
| Active (I/O in flight) | Fast blink at 4 Hz |
Additional resources
Primary documentation resources:
- NetScaler hardware platforms documentation: Complete hardware documentation, including detailed specifications, configuration guides, and troubleshooting procedures.
- System upgrade and downgrade guide: Step-by-step procedures for upgrading or downgrading software while maintaining system availability and configuration integrity.
- High availability configuration guide: Detailed instructions for implementing high availability configurations using multiple NetScaler appliances for enhanced system resilience.
Support information
When contacting NetScaler Support, prepare the following information:
- Hardware serial number: Located on the chassis label (required for all support cases).
- Software version: Current software builds and version information.
- Problem description: Detailed description of the issue, including error messages.
- System configuration: Network topology and relevant configuration details.
- Log files: System logs and diagnostic information, if available.