
Automated certificate management with cert-manager
NetScaler Ingress Controller supports automatic provisioning and renewal of TLS certificates using cert-manager. The
cert-manager is a native Kubernetes certificate management controller. It issues certificates from different sources, such as Let’s Encrypt and HashiCorp Vault.
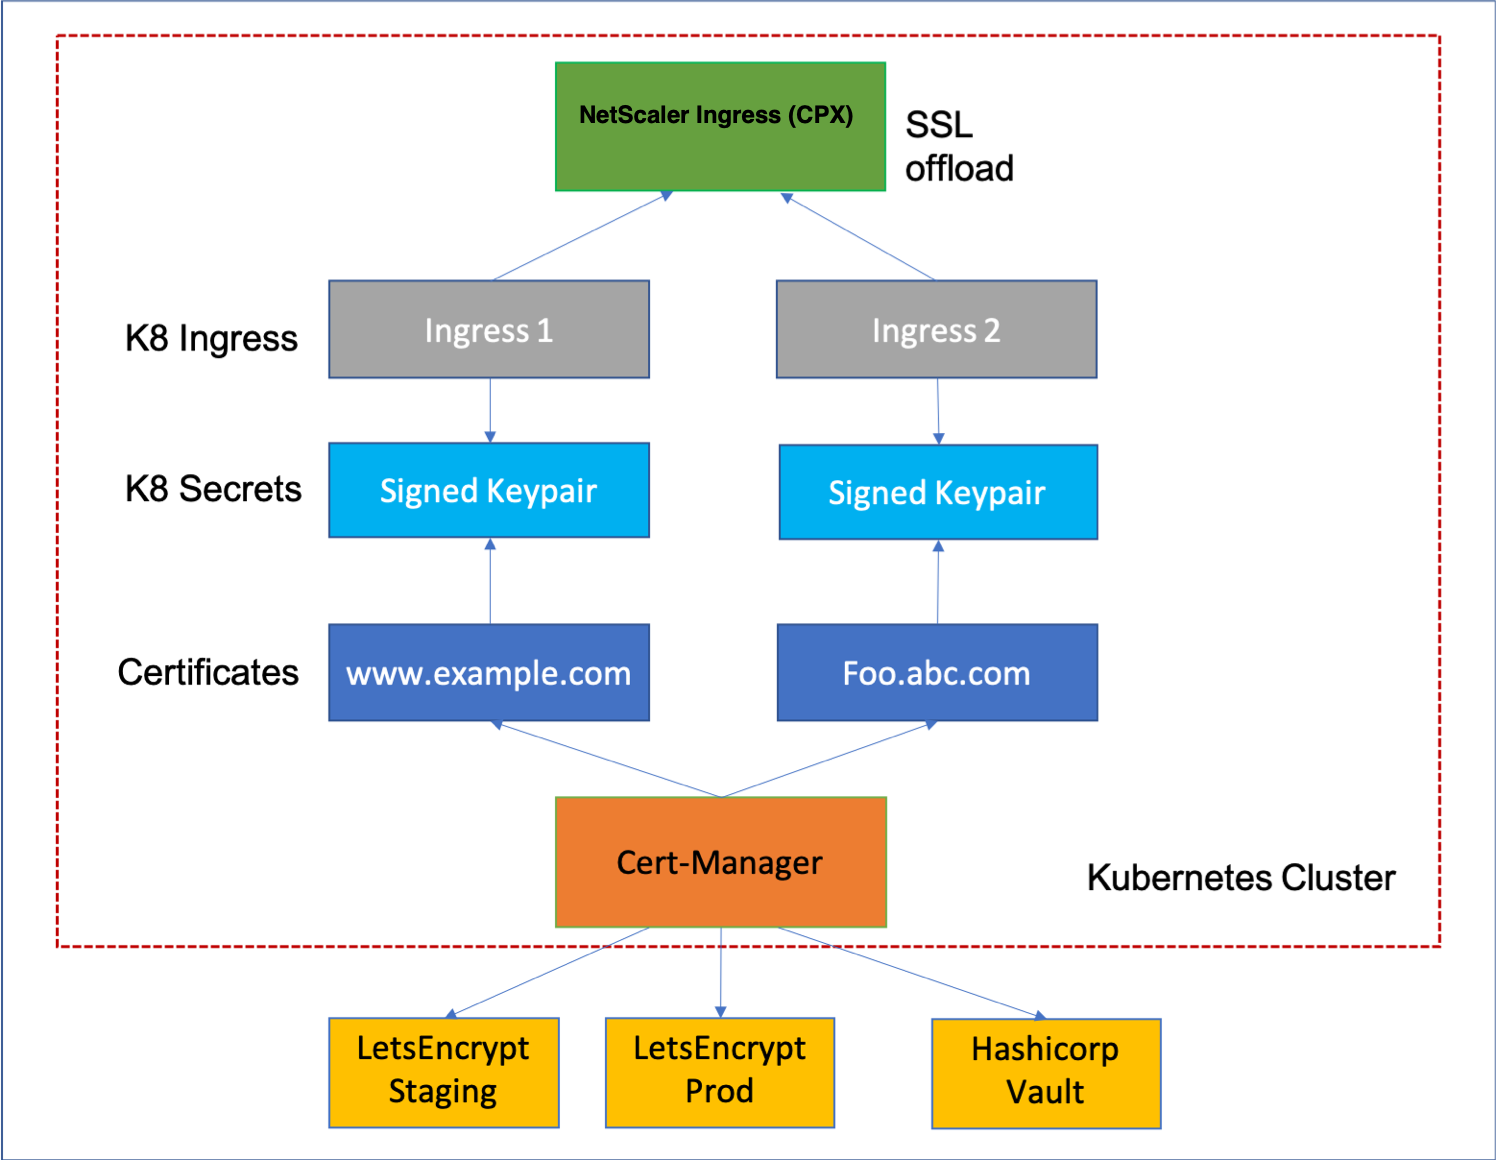
As shown in the following diagram,
cert-manager interacts with the external Certificate Authorities (CA) to sign the certificates and converts it to Kubernetes secrets. These secrets are used by NetScaler Ingress Controller to configure SSL virtual server on the NetScaler.
For detailed configurations, refer: