
Deploy NetScaler Ingress Controller in OpenShift using NetScaler Operator
In this setup, NetScaler Ingress Controller configures NetScaler MPX or NetScaler VPX residing outside the OpenShift cluster.
Prerequisites
-
Red Hat OpenShift Cluster (version 4.11 or later).
-
Deploy NetScaler Operator. For information on how to deploy NetScaler Operator, see Deploy NetScaler Operator.
-
Identify the IP address that NetScaler Ingress Controller needs to communicate with NetScaler. This IP address might be any one of the following IP addresses depending on the type of NetScaler deployment:
-
NSIP (for standalone appliances) - The management IP address of a standalone NetScaler appliance. For more information, see IP Addressing in NetScaler.
-
SNIP (for appliances in High Availability mode) - The subnet IP address. For more information, see IP Addressing in NetScaler.
-
CLIP (for appliances in Cluster mode) - The cluster management IP (CLIP) address for a clustered NetScaler deployment. For more information, see IP addressing for a cluster.
-
-
The user name and password of NetScaler VPX or NetScaler MPX used as the ingress device. NetScaler must have a system user account (non-default) with certain privileges so that the NetScaler Ingress Controller can configure NetScaler VPX or NetScaler MPX. For instructions to create a system user account on NetScaler, see Create system user account for NetScaler Ingress Controller in NetScaler.You can directly pass the user name and password as environment variables to the controller, or use OpenShift secrets (recommended). To create a secret for the user name and password using the following command, modify the
<username>and<password>to required values:oc create secret generic nslogin --from-literal=username=<username> --from-literal=password=<password> -
To export to any service monitor, install the service monitor CRD by using the following command:
oc create -f https://raw.githubusercontent.com/prometheus-operator/prometheus-operator/refs/heads/main/example/prometheus-operator-crd/monitoring.coreos.com_servicemonitors.yaml
Deploy NetScaler Ingress Controller as a standalone pod using NetScaler Operator
Using NetScaler Operator you can deploy NetScaler Ingress Controller as a standalone pod in an OpenShift cluster. NetScaler Ingress Controller configures NetScaler MPX or NetScaler VPX, which is deployed as an ingress device or router for an application running in the OpenShift cluster. The following diagram explains the topology:
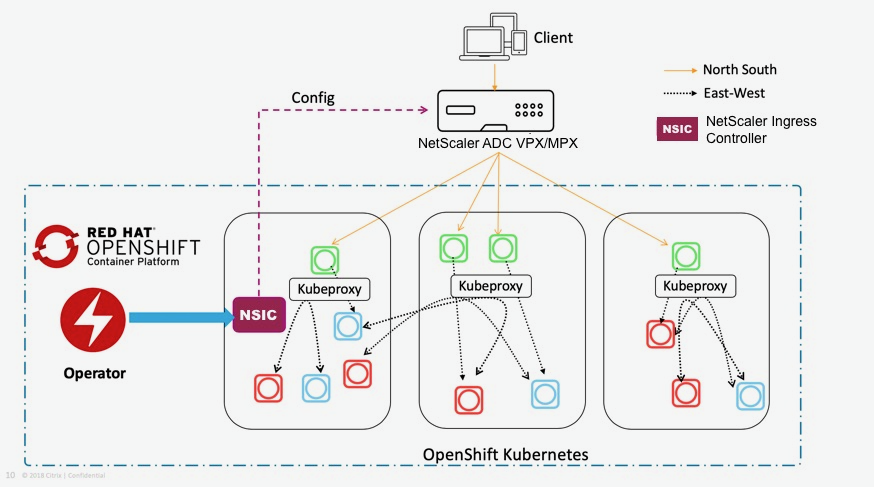
Perform the following steps:
-
Log in to the OpenShift 4.x Cluster console.
-
Deploy an Apache application using the console.
-
Navigate to Workloads > Deployments > Create Deployment and use the following YAML file to create the deployment.NOTE:The Apache application is for the demonstration purpose only. You can modify the YAML file based on your requirement.
---
 apiVersion: apps/v1
 kind: Deployment
 metadata:
   name: apache
   labels:
       name: apache
 spec:
   selector:
     matchLabels:
       app: apache
   replicas: 2
   template:
     metadata:
       labels:
         app: apache
     spec:
       containers:
       - name: apache
         image: httpd:latest
         ports:
- containerPort: 80 -
Navigate to Workloads > Pods section and ensure that the Apache application pods are up and running.
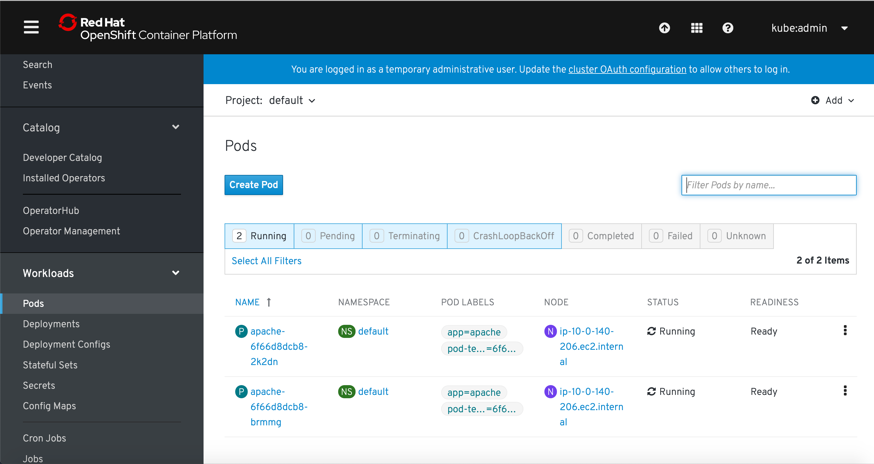
-
-
Create a service for the Apache application. Navigate to Networking > Services > Create Service and use the following YAML file.
apiVersion: v1
 kind: Service
 metadata:
   name: apache
 spec:
   ports:
   - port: 80
     targetPort: 80
   selector:
     app: apache
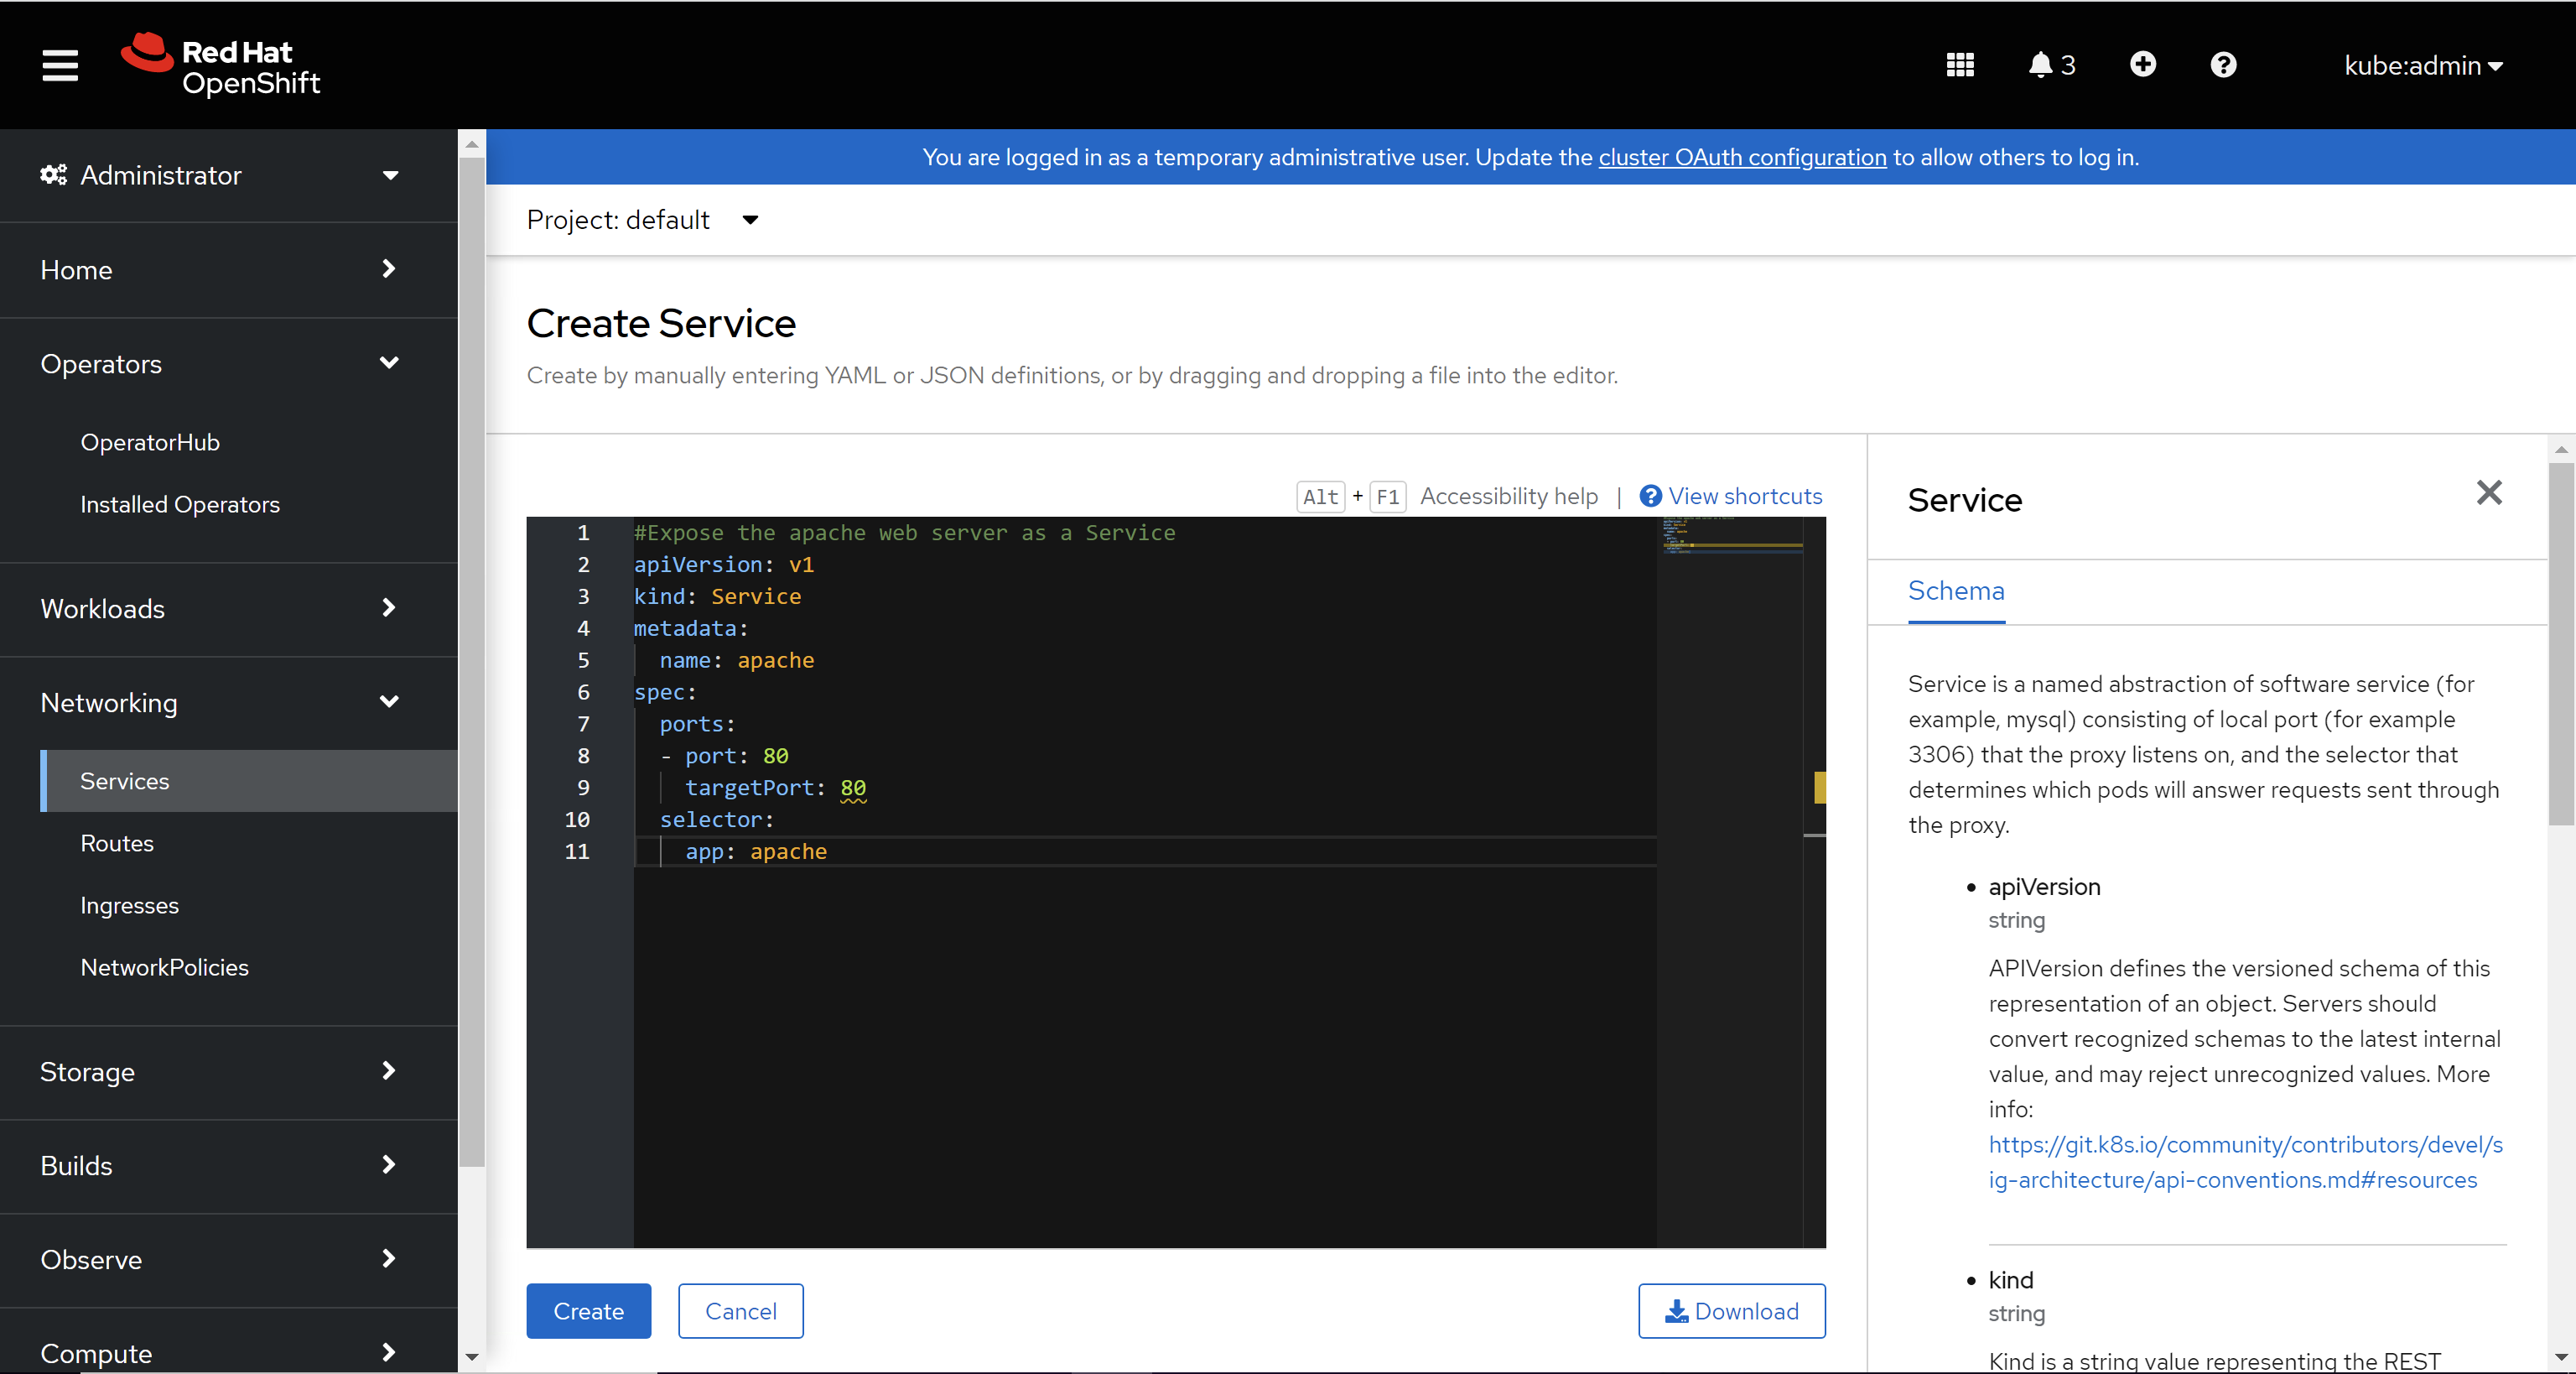
-
Create an ingress for the Apache application. Navigate to Networking > Ingress > Create Ingress and use the following YAML to create the ingress. Ensure that you update the VIP address of NetScaler VPX in the ingress YAML before applying it in the cluster.
apiVersion: networking.k8s.io/v1
 kind: Ingress
 metadata:
   annotations:
     ingress.citrix.com/frontend-ip: <NSVIP>
   name: vpx-ingress
 spec:
   ingressClassName: nsic-vpx
   rules:
   - host: citrix-ingress-operator.com
     http:
       paths:
       - backend:
           service:
             name: apache
             port:
               number: 80
         path: /
         pathType: Prefix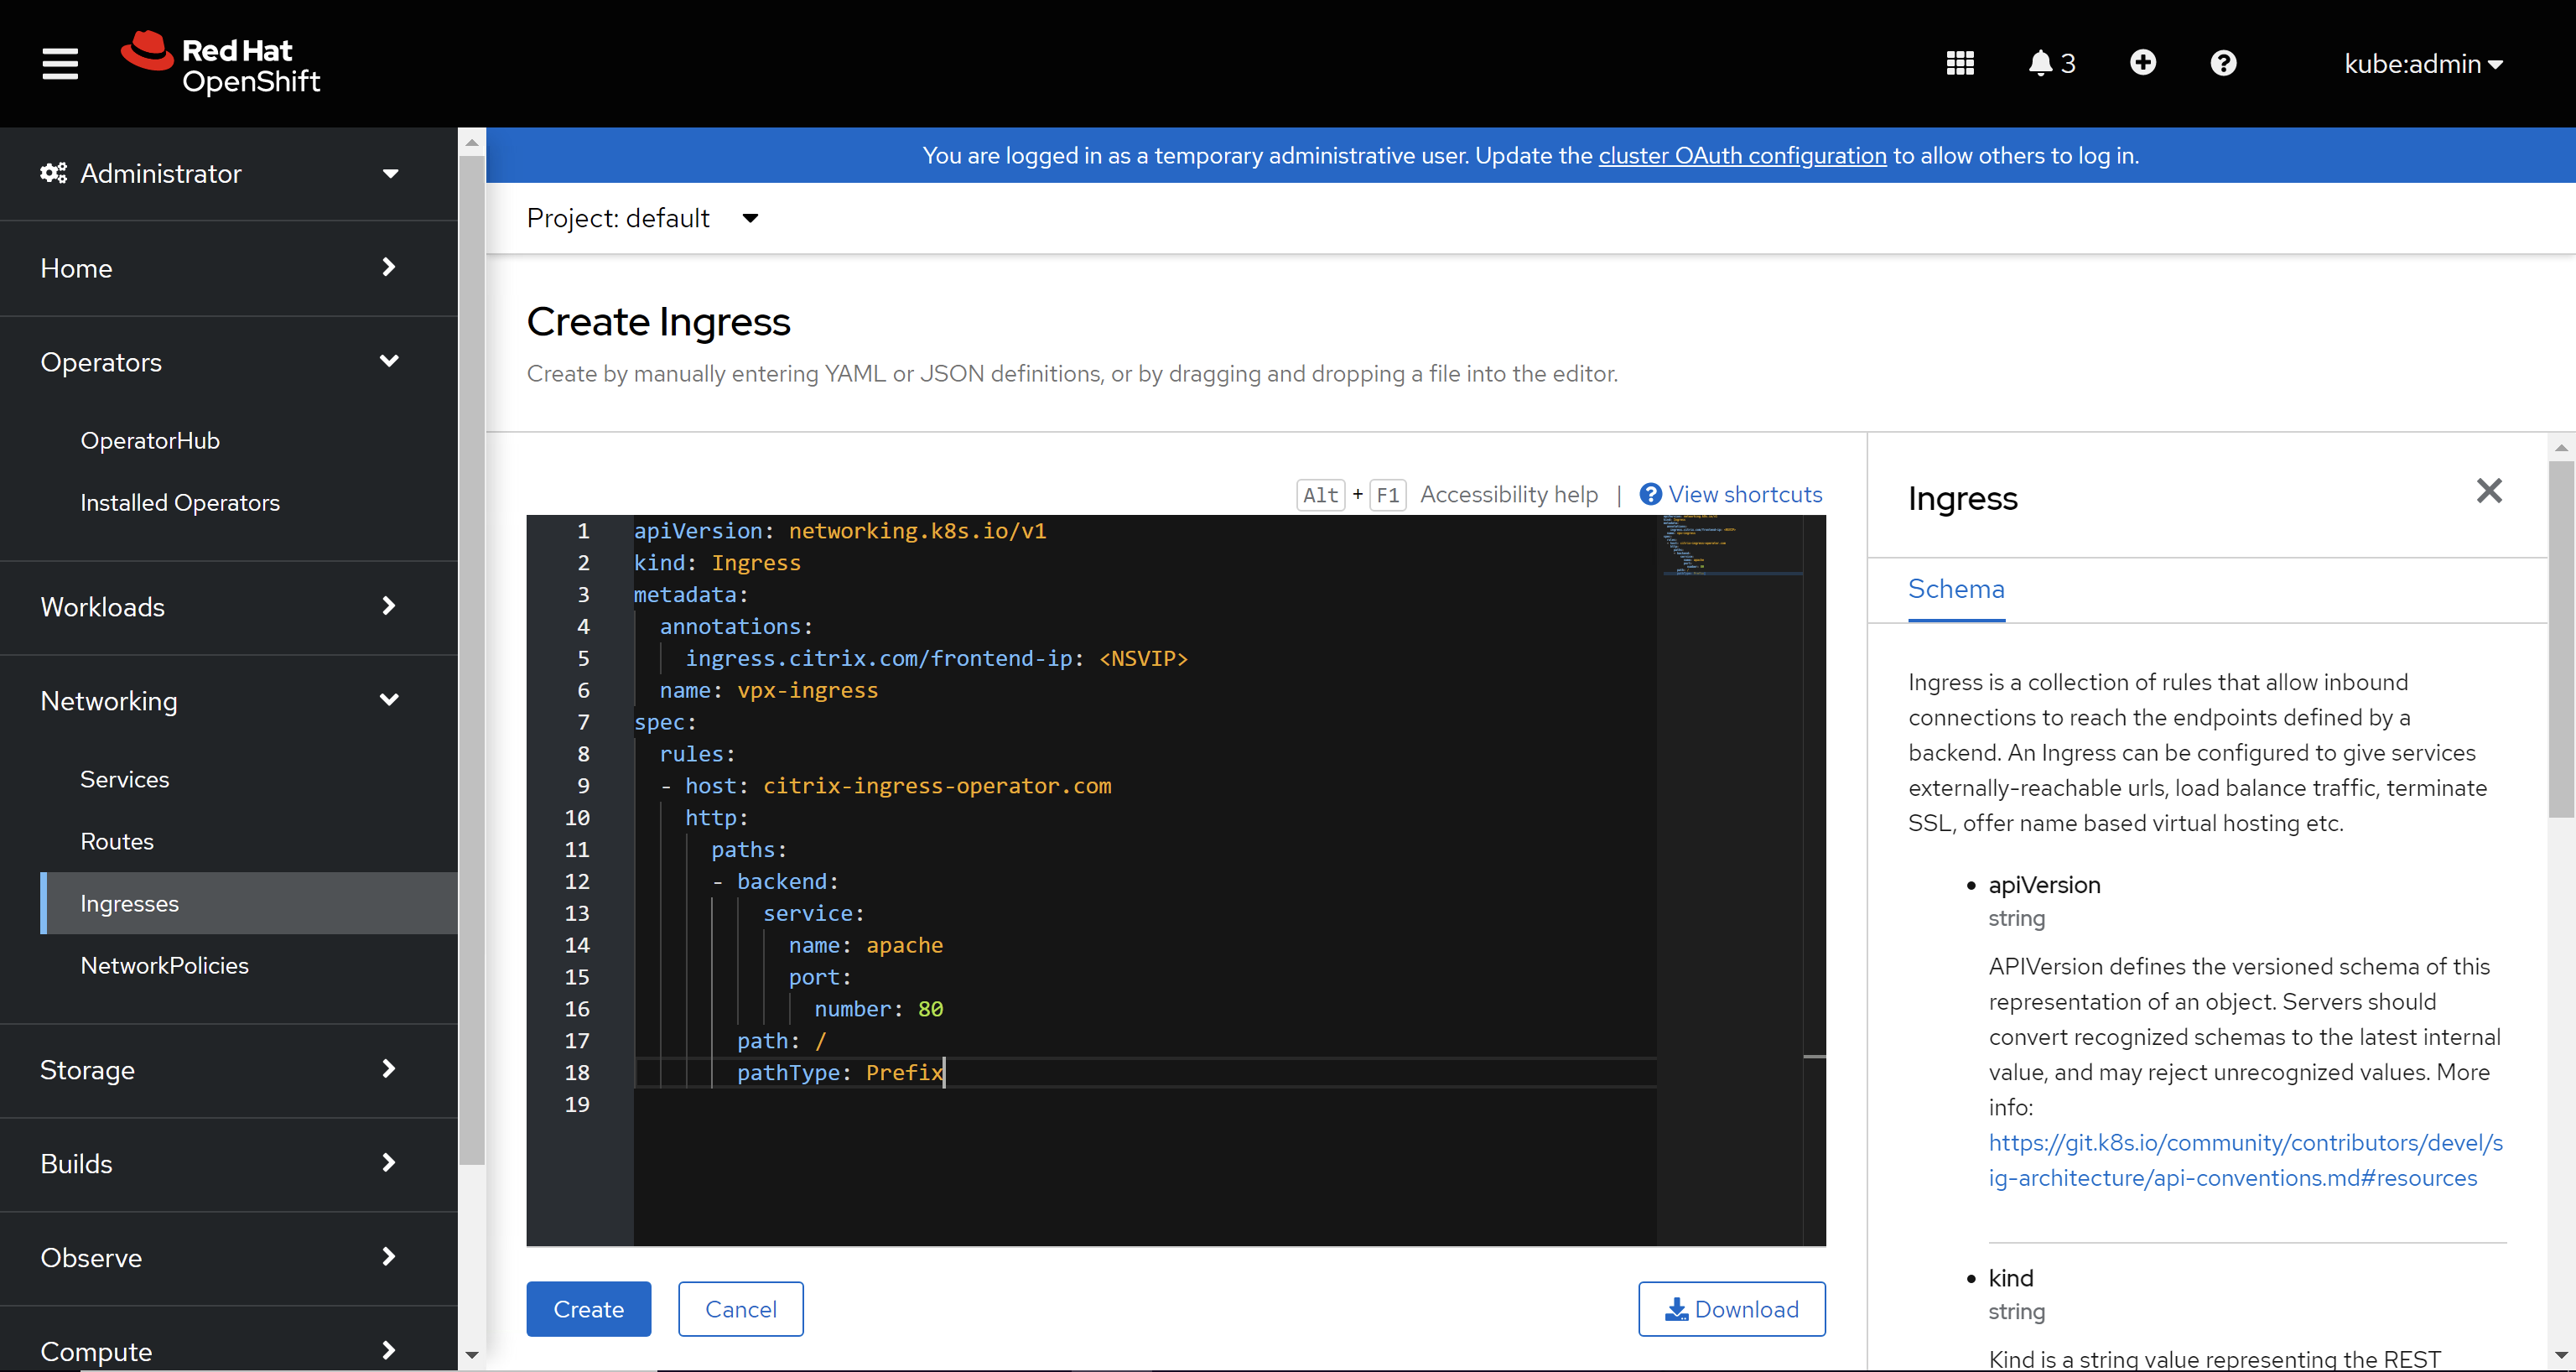
-
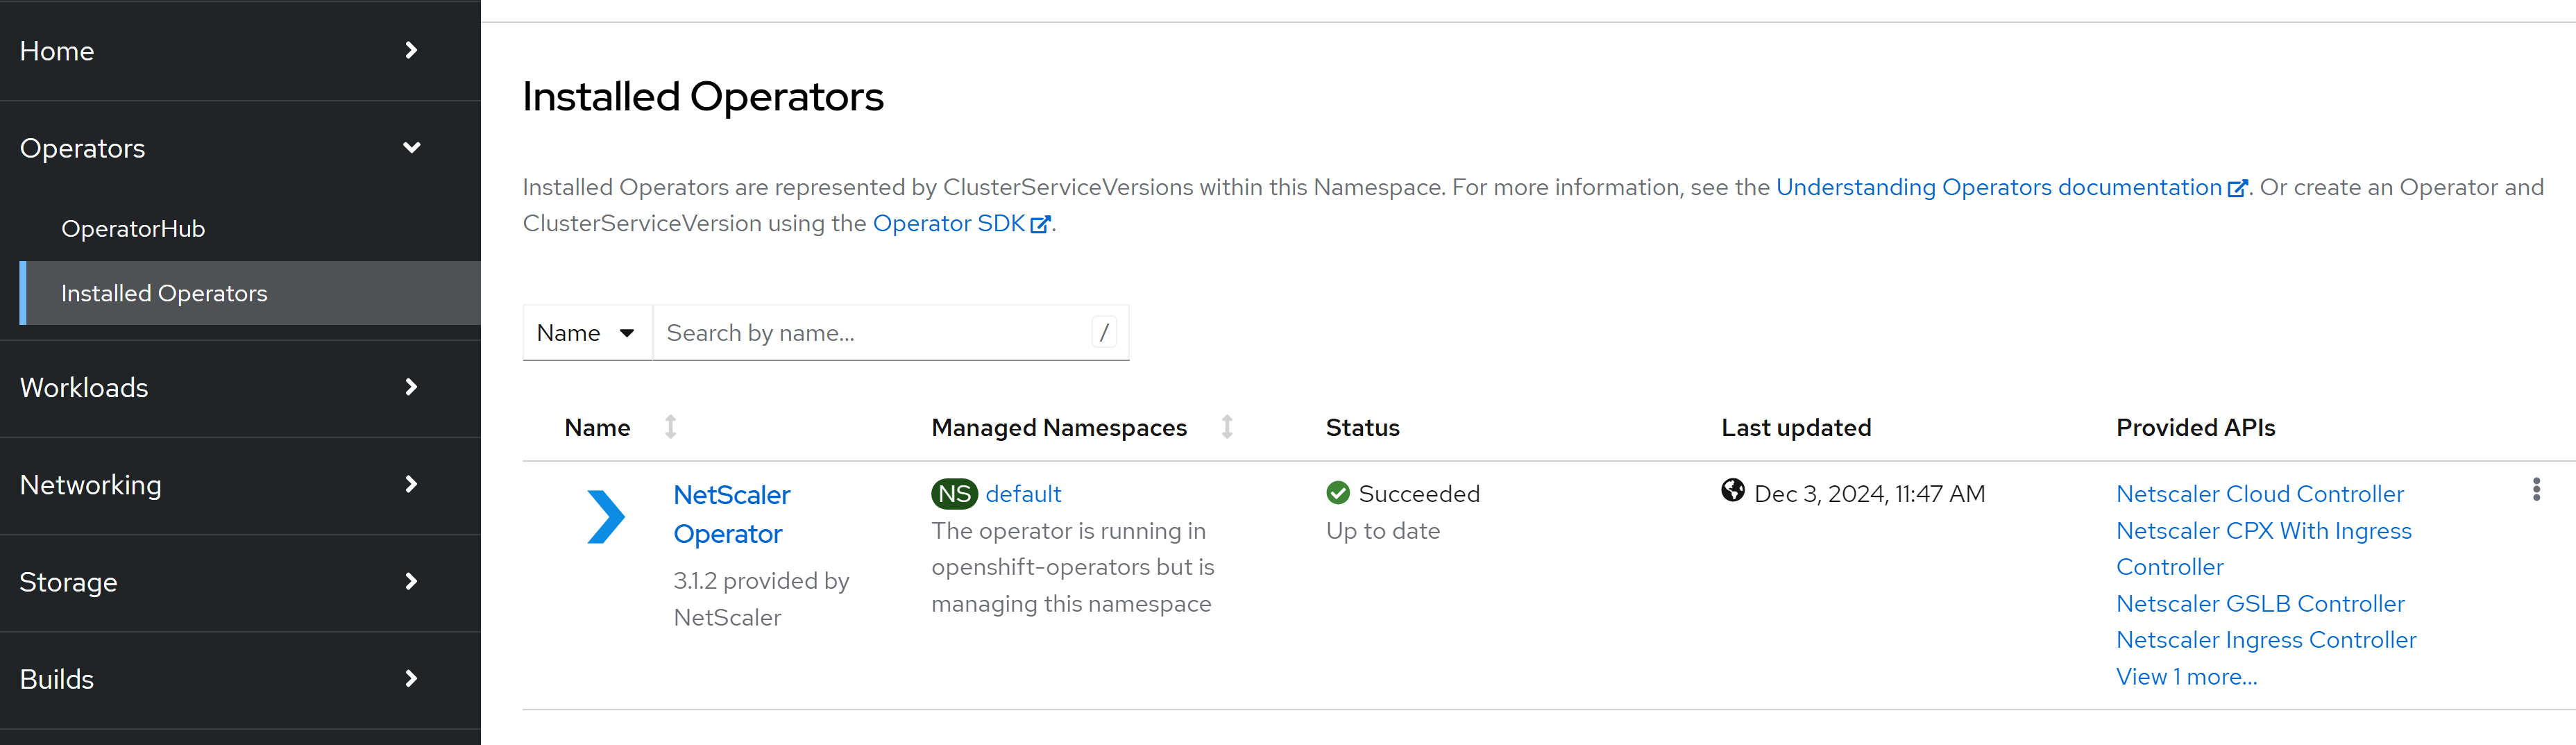
Navigate to Operators > Installed Operators and click NetScaler® Operator.
-
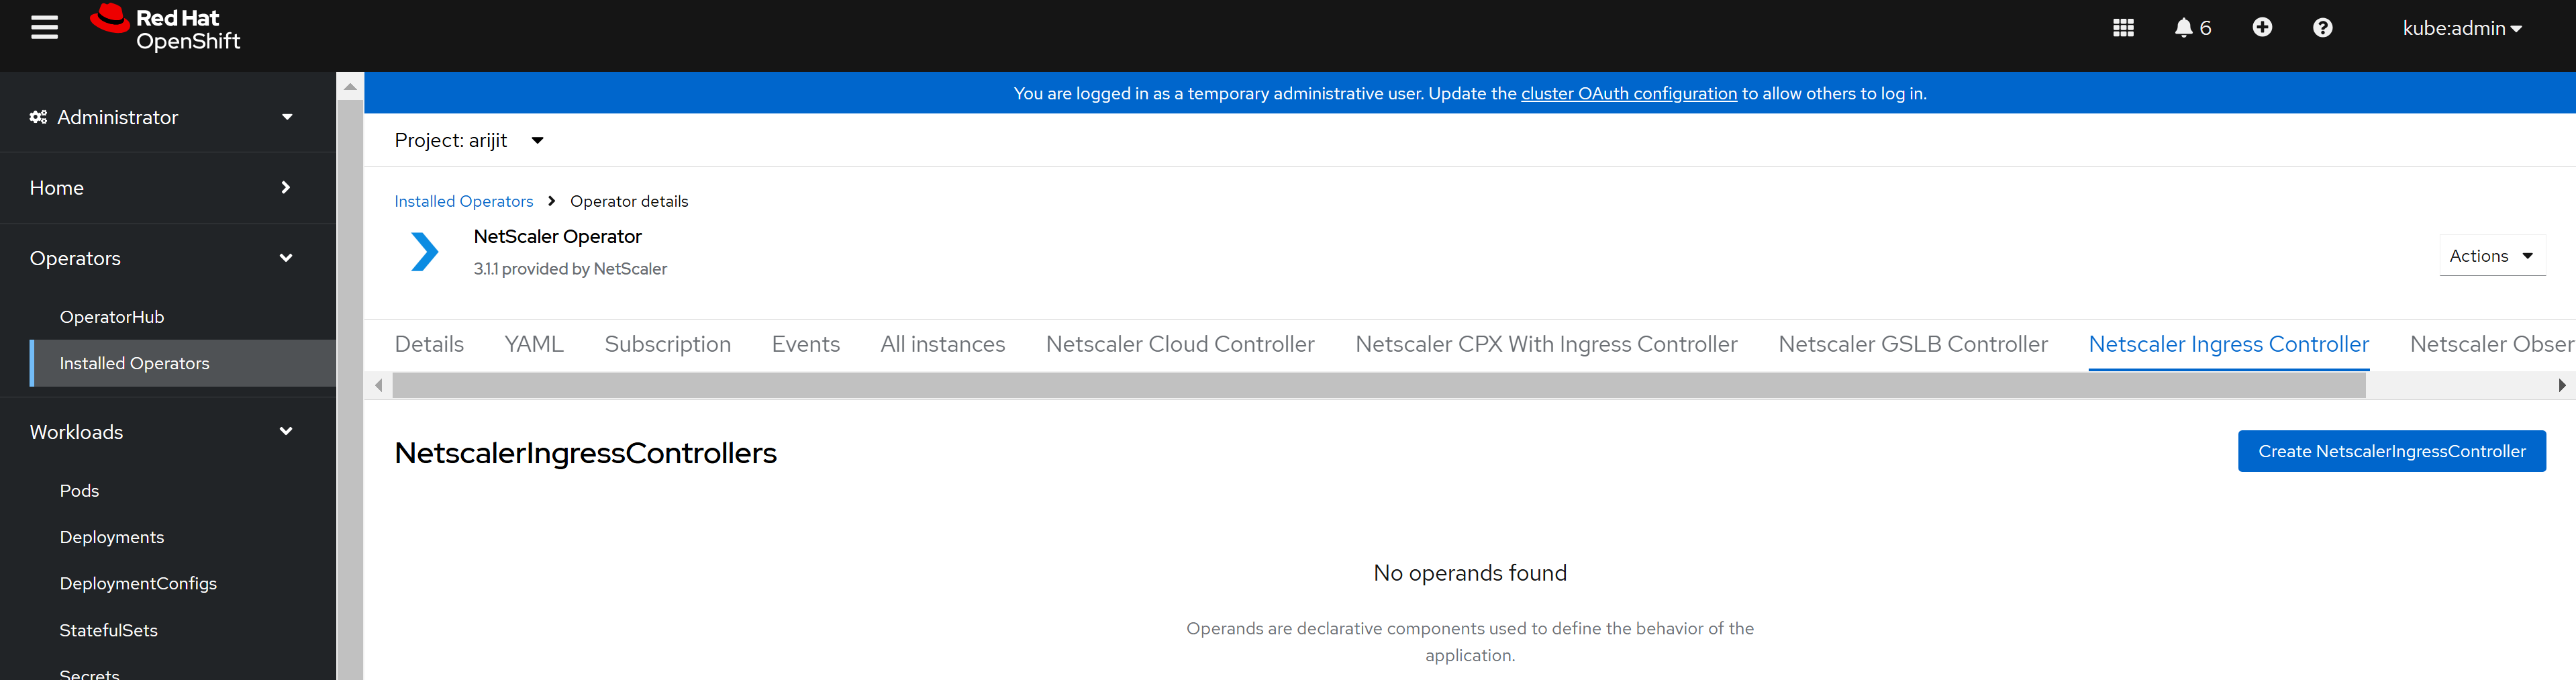
Click the NetScaler Ingress Controller tab and select Create NetScalerIngressController.
 The NetScaler Ingress Controller YAML definition is displayed. Optionally, you can select
Form viewbutton and update the parameters in a form.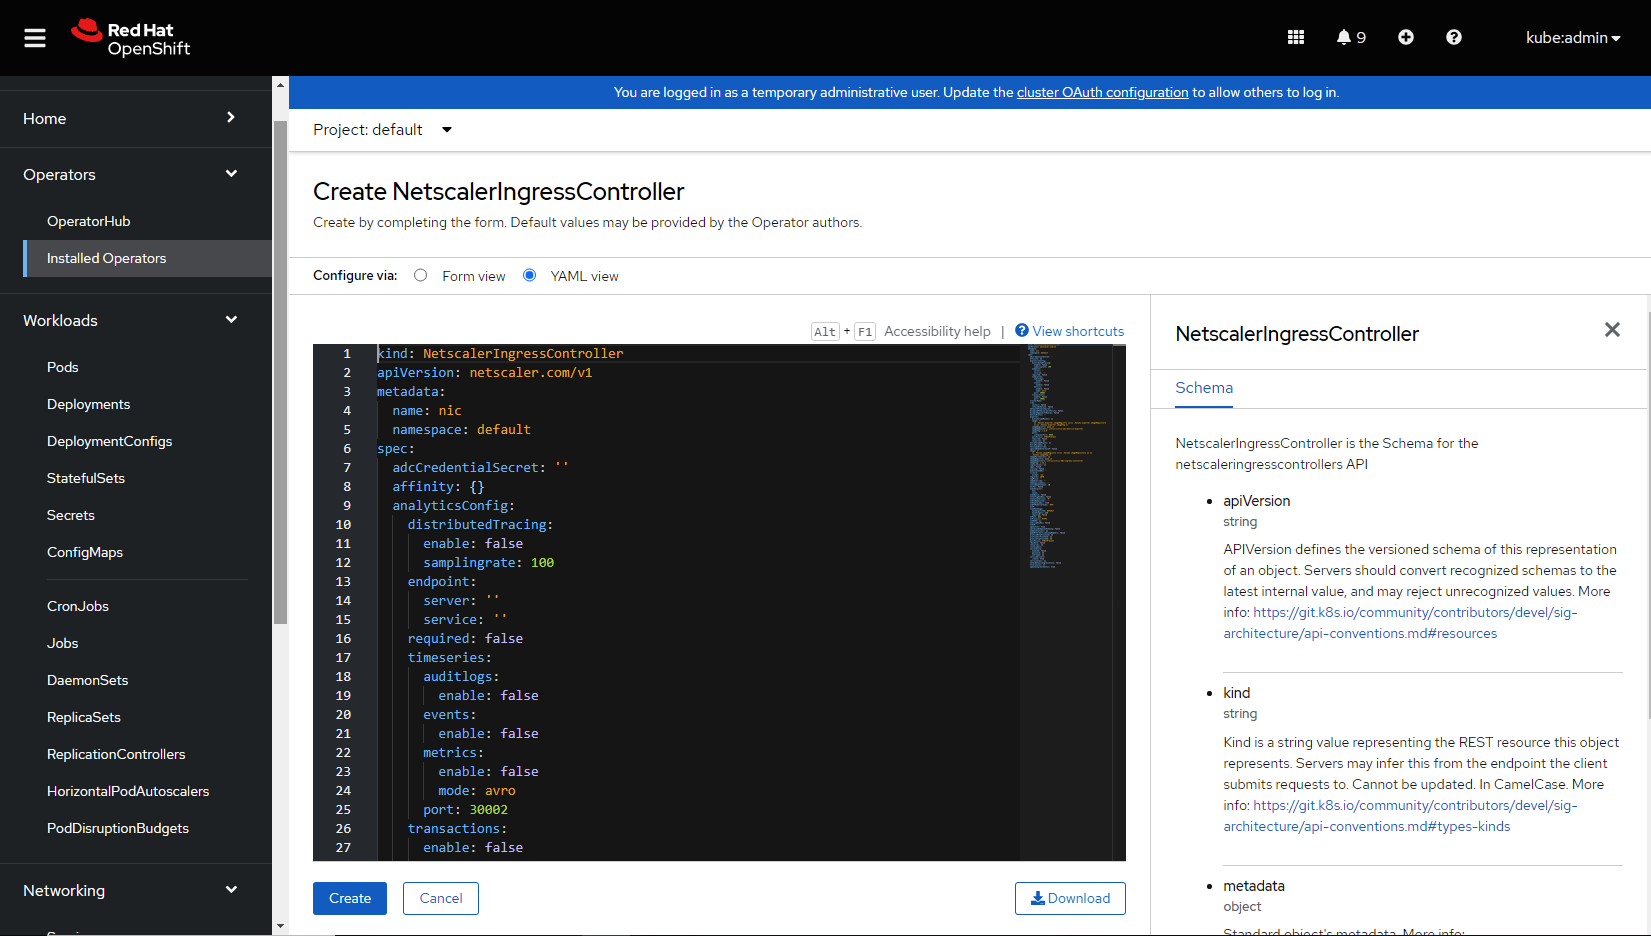
-
Refer the following table that lists the mandatory and optional parameters that you can configure during installation.Note:
-
Ensure that the
acceptLicenseparameter is set toYes. -
Specify a unique value for
entityPrefix. -
Provide the IP address of NetScaler VPX instance for
nsIPparameter and Kubernetes secret created using NetScaler VPX credentials inadcCredentialSecretparameter. -
To associate NetScaler Ingress Controller with the ingress resource specified in this procedure, provide the ingress class name using the
ingressClassparameter asingressClass: ['nsic-vpx']. -
Optionally, you can click the
form viewand set the parameters as required.
You can configure other available parameters depending on your use case.Parameters Mandatory or Optional Default value Description acceptLicense Mandatory No Set this value to Yesto accept the NetScaler Ingress Controller EULA.affinity Optional N/A Affinity labels for pod assignment. extraVolumes Optional N/A Additional volumes for the pod. Mount them by using extraVolumeMounts.imagePullSecrets Optional N/A List of names of Kubernetes secrets to be used for pulling the images from a private Docker registry or repository. The operator adds these secrets to the service account that it creates. For more information on how to create this secret, see Pull an Image from a Private Registry. nodeSelector Optional N/A The node label key:value pair to be used for nodeSelector option in NetScaler Ingress Controller deployment. podAnnotations Optional N/A Map of annotations to add to the pods. tolerations Optional N/A The tolerations for the NetScaler Ingress Controller deployment. extraContainers / extraEnv / initContainers / hostAliases Optional N/A Extra pod-spec hooks to add sidecar containers, environment variables, init containers, and host aliases to the pod. apiPriorityAndFairness Optional enabled falseConfigure Kubernetes API Priority and Fairness for requests from NetScaler Ingress Controller to the Kubernetes API server. Set apiPriorityAndFairness.enabledtotrueto enable it, and use theflowSchemaandpriorityLevelConfigurationfields to tune it.createClusterRoleAndBinding Optional true Set this parameter to falseto skip creating the ClusterRole and ClusterRoleBinding for NetScaler Ingress Controller.serviceAccount Optional create trueConfigure the service account for the NetScaler Ingress Controller pod. Use serviceAccount.createto control whether a service account is created andserviceAccount.nameto use an existing one.tokenExpirationSeconds Optional 31536000 The expiration time, in seconds, for the service account token that is projected into the NetScaler Ingress Controller pod. upgradeImageAlways Optional true When true(the default), the operator deploys the images that are built into this operator release and ignores the image values in this resource. Set it tofalseto deploy the images that you specify.Parameter Mandatory/Optional Default value Description : analyticsConfig: distributedTracing.enable Optional false Set this value to trueto enable OpenTracing in NetScaler.distributedTracing.samplingRate Optional 100 OpenTracing sampling rate in percentage. required Optional false Set this value to trueif you want to configure NetScaler to send metrics and transaction records to the analytics server.endpoint.metrics.service Optional N/A The IP address or DNS address of the analytics server. Format: servicename.namespace,servicename.namespace.svc.cluster.local,namespace/servicename.endpoint.transactions.service Optional N/A An IP address or a service name with the namespace of the analytics service deployed in the Kubernetes environment. Format: namespace/servicename.timeseries.port Optional 30002 The port used to expose the analytics service outside the cluster for a time-series endpoint. timeseries.auditLogs.enable Optional false Set this value to trueto export audit log data from NetScaler.timeseries.events.enable Optional false Set this value to trueto export events from NetScaler.timeseries.metrics.enable Optional false Set this value to trueto enable sending metrics from NetScaler.timeseries.metrics.mode Optional avro Mode of the metric endpoint. Possible values are avro,prometheus, andinflux.timeseries.metrics.exportFrequency Optional 30 Time interval for exporting time-series data. Possible values range from 30 to 300 seconds. timeseries.metrics.schemaFile Optional schema.json Name of a schema file with the required NetScaler counters to be added and configured for metrics collector. A reference schema file reference_schema.jsonwith all the supported counters is also available in the path/var/metrics_conf/. This schema file can be used as a reference to build a custom list of counters.timeseries.metrics.enableNativeScrape Optional false Set this value to truefor native export of metrics.transactions.port Optional 30001 The port used to expose analytics service outside the cluster for a transaction endpoint. transactions.enable Optional false Set this value to trueto export transactions from NetScaler.Parameter Mandatory/Optional Default value Description : exporter: extraVolumeMounts Optional N/A Additional VolumeMounts to be mounted in the exporter container. image Optional quay.io/netscaler/netscaler-adc-metrics-exporter@sha256:a994d1de39c4dda24d92dbb77c0fcbb224b71e80ac80dfddad268072739c76c5The metrics exporter image hosted on Quay.io. Used only when upgradeImageAlwaysisfalse.required Optional false Set to trueto run the Exporter for NetScaler Stats along with NetScaler Ingress Controller to pull metrics for the NetScaler MPX or NetScaler VPX.pullPolicy Optional IfNotPresent The exporter image pull policy. ports.containerPort Optional 8888 The exporter container port. resources Optional N/A CPU/memory resources for a metrics exporter container. serviceMonitorExtraLabels Optional N/A Extra labels for a service monitor when exporter is enabled. validateCert Optional no Controls whether the metrics exporter validates the NetScaler certificate. Set it to auto(oryes,true,y,on, or1) to validate the certificate against the trust store in the exporter image. This requires metrics exporter 1.7.0 or later. Set it tono(orfalse,n,off, or0) to turn off validation. The operator rejects any other value. Leaving this parameter unset is not an error: the defaultnoapplies, so an existing resource keeps its previous behavior after an upgrade. WheningressController.nsValidateCertis configured, the exporter validates against that CA instead.Parameter Mandatory/Optional Default value Description : ingressController: clusterName Optional N/A A unique identifier of the Kubernetes cluster on which NetScaler Ingress Controller is deployed. defaultSSLCertSecret Optional N/A Kubernetes secret name that needs to be used as a default non-SNI certificate in NetScaler. defaultSSLSNICertSecret Optional N/A Kubernetes secret name that needs to be used as a default SNI certificate in NetScaler. disableAPIServerCertVerify Optional false Set this parameter to Truefor disabling API Server certificate verification.disableOpenshiftRoutes Optional false By default OpenShift routes are processed in the OpenShift environment. This parameter can be used to disable NetScaler Ingress Controller processing the OpenShift routes. enableLivenessProbe Optional true Set to falseto disable liveness probe settings for NetScaler Ingress Controller.enableReadinessProbe Optional true Set to falseto disable readiness probe settings for NetScaler Ingress Controller.entityPrefix Mandatory N/A The prefix for the resources on NetScaler MPX or NetScaler VPX. Specify a unique value for each NetScaler Ingress Controller that shares a NetScaler. ignoreNodeExternalIP Optional False While adding node IP address as a service group member for type LoadBalancer services or NodePort services, NetScaler Ingress Controller has a selection criteria where it chooses Node ExternalIPif available andNode InternalIPifNode ExternalIPis not available. But some users might want to use Node InternalIP over Node ExternalIP even if Node ExternalIP is present. If this variable is set totrue, NSIC prioritizes the Node InternalIP to be used for service group members even if Node ExternalIP is present.image Mandatory quay.io/netscaler/netscaler-k8s-ingress-controller@sha value of latest releaseThe NetScaler Ingress Controller image hosted on Quay.io. Used only when upgradeImageAlwaysisfalse.ingressClass Optional N/A Parameter to associate a particular ingress resource with NetScaler Ingress Controller. For more information on ingress class, see Ingress class support. For Kubernetes version >= 1.19, this parameter creates an IngressClass object with the name specified here. extraVolumeMounts Optional N/A Additional VolumeMounts to be mounted in the NetScaler Ingress Controller container. ipam Optional false Set this parameter to trueto use the IPAM controller to automatically allocate an IP address to the service of type LoadBalancer.jsonLog Optional false Set this argument to true if log messages are required in the JSON format. kubernetesURL Optional N/A The kube-apiserver url that NetScaler Ingress Controller uses to register the events. If the value is not specified, NetScaler Ingress Controller uses the internal kube-apiserver IP address. livenessProbe Optional initialDelaySeconds 50, periodSeconds60, failureThreshold3, successThreshold1Liveness probe settings for NetScaler Ingress Controller. logLevel Optional INFO The log level to control the logs generated by NetScaler Ingress Controller. The supported log levels are DEBUG,INFO,WARNING, andERROR.logProxy Optional N/A Elasticsearch or Kafka or Zipkin endpoint for NetScaler observability exporter. multiClusterPrefix Optional mc The prefix for the shared resources on NetScaler MPX or NetScaler VPX for multicluster ingress feature. NetScaler Ingress Controllers that are collaboratively sharing the content switching virtual server IP address must be configured with the same value for multiclusterPrefix. For more information see this. namespaceLabels Optional N/A Provide the namespace labels selectors to be used by NetScaler Ingress Controller for routeSharding in the OpenShift cluster. nodeLabels Optional N/A If there are pods on nodes with node labels, NetScaler Ingress Controller configures NetScaler to advertise the VIP using BGP. nodeWatch Optional false Set the parameter to trueif you want to automatically configure network route from NetScaler MPX or NetScaler VPX to the pods in the Kubernetes cluster. For more information, see Automatically configure route on the NetScaler instance.nsncPbr Optional false Set this parameter to trueto inform NetScaler Ingress Controller that NetScaler Node Controller is configuring Policy Based Routes (PBR) on NetScaler. For more information, see NSNC-PBR-SUPPORTopenshift Optional true Set this parameter to falseif the OpenShift environment is not being used.optimizeEndpointBinding Optional false Set this parameter to trueto enable binding of back-end endpoints to a service group in a single API-call. Recommended when endpoints (pods) per application are large in number. Applicable only for NetScaler version >=13.0-45.7.podIPsforServiceGroupMembers Optional false By default, NetScaler Ingress Controller adds node IP address and node port as service group members while configuring type LoadBalancer Services and NodePort services. If set to TrueNetScaler Ingress Controller adds pod IP address and pod port instead of node IP address and node port. You can set this parameter totrueif there is a route between NetScaler and K8s clusters internal pods either using feature-node-watch argument or using NetScaler Node Controller.profileHttpFrontend Optional N/A The front-end HTTP profile can be configured in one of two ways: inline via config, or by an existing preconfigured profile. Empty value is also allowed. For details, see Configuration using FRONTEND_HTTP_PROFILE. profileSslFrontend Optional N/A The front-end SSL profile can be configured in one of two ways: inline via config, or by an existing preconfigured profile. Empty value is also allowed. profileSslFrontend.bindings.cipherscan only be used with config. For details, see Configuration using FRONTEND_SSL_PROFILE.profileTcpFrontend Optional N/A The front-end TCP profile can be configured in one of two ways: inline via config, or by an existing preconfigured profile. Empty value is also allowed. For details, see Configuration using FRONTEND_TCP_PROFILE. pullPolicy Optional IfNotPresent The NetScaler Ingress Controller image pull policy. rbacRole Optional false Set this parameter to trueto deploy NetScaler Ingress Controller with RBAC role set rbacRole=true; by default NetScaler Ingress Controller gets installed with RBAC ClusterRole(rbacRole=false).readinessProbe Optional initialDelaySeconds 50, periodSeconds60, failureThreshold3, successThreshold1Readiness probe settings of NetScaler Ingress Controller. resources Optional requests: cpu 32m, memory256MiCPU/memory resources for the NetScaler Ingress Controller container. routeLabels Optional N/A The route labels selectors to be used by NetScaler Ingress Controller for routeSharding in OpenShift cluster. serviceClass Optional N/A Parameter used to associate only specific services to NetScaler Ingress Controller if multiple ingress controllers are deployed. For more information on service class, see Service class support. setAsDefaultIngressClass Optional False Sets the IngressClass object as the default ingress class. New ingresses without an "ingressClassName" field specified will be assigned this ingress class. This parameter is applicable only for Kubernetes versions >= 1.19. updateIngressStatus Optional true Set this parameter if Status.LoadBalancer.Ingressfield of the ingress resources managed by NetScaler Ingress Controller needs to be updated with allocated IP addresses. For more information see this.bgpAdvertisement Optional false Set this parameter to trueto enable NetScaler Ingress Controller to advertise the VIP using BGP.certBundle Optional false Set this parameter to trueto enable the certificate bundle feature on NetScaler.clearStaleServiceStatus Optional false Performs a one-time retraction, at startup, of a service status that this controller published before updateServiceStatuswas set tofalse. RequiresupdateServiceStatusto also be set tofalse.nodeWatchLabelSelector Optional N/A Filters which nodes nodeWatchprograms routes for. Applied only whennodeWatchis set totrueand this value is non-empty. Specify a map of node labels, for examplenodeWatchLabelSelector: {kubernetes.io/os: linux}. Only nodes that have all these labels are used.nsValidateCert Optional N/A Configures validation of the NetScaler server certificate for the connection from NetScaler Ingress Controller. Set nsValidateCert.nsCertSecretto a Kubernetes secret that stores the CA certificate under the keynsCA.pem(for example,oc create secret generic nscacert --from-file=nsCA.pem=<ca-file>). You must also sethostAliasesto map thensIPaddress to the host name in the NetScaler certificate; otherwise, the operator does not deploy NetScaler Ingress Controller. The operator addshostAliasesto the pod only whennsValidateCert.nsCertSecretis set. When the metrics exporter is enabled, it validates the certificate against the same CA.updateServiceStatus Optional true Set this parameter to falseto stop publishing the NetScaler LoadBalancer VIP into the status of a type LoadBalancer service.Parameter Mandatory/Optional Default value Description : netscaler: adcCredentialSecret Optional N/A Name of the Kubernetes secret that holds the NetScaler user name and password (keys usernameandpassword). Set either this parameter orsecretStore, but not both. You do not need either one whenvaultCredentialssupplies the credentials.nitroReadTimeout Optional 20 The nitro read timeout in seconds. nsConfigDnsRec Optional false Set to trueto enable DNS address record addition in NetScaler through ingress.nsCookieVersion Optional 0 The persistence cookie version (0 or 1). nsDnsNameserver Optional N/A DNS nameservers in NetScaler. nsHttp2ServerSide Optional OFF Set this parameter to ONfor enabling HTTP2 for NetScaler service group configurations.nsIP Mandatory N/A NetScaler IP address. nsLbHashAlgo.required Optional false Set this parameter to trueto configure the load balancing consistent hashing algorithm.nsLbHashAlgo.hashFingers Optional 256 The number of fingers to be used for the hashing algorithm. Possible values are from 1 to 1024. nsLbHashAlgo.hashAlgorithm Optional default The supported algorithm. The supported algorithms are default,jarh, andprac.nsPort Optional 443 The port used by NetScaler Ingress Controller to communicate with NetScaler. You can use port 80 for HTTP. nsProtocol Optional HTTPS The protocol used by NetScaler Ingress Controller to communicate with NetScaler. You can use HTTP on port 80. nsSNIPs Optional N/A The list of subnet IP addresses on the NetScaler, which is used to create PBR routes instead of static routes PBR support nsSvcLbDnsRec Optional false Set this parameter to trueto enable DNS address record addition in NetScaler through type LoadBalancer Service.nsVIP Optional N/A The virtual IP address on NetScaler. secretStore Optional N/A Defines the NetScaler user name and password as references (for example, a Kubernetes secret, a ConfigMap, or a pod field) instead of using adcCredentialSecret. Set bothsecretStore.usernameandsecretStore.password.vaultCredentials Optional N/A Reads the NetScaler user name and password from files that a Vault Agent sidecar writes to a shared in-memory volume. The operator does not deploy the Vault Agent; add it by using extraContainers. Fields:enabled(defaultfalse),mountPath(default/etc/citrix),credentialWaitSeconds(default120),suppressEnvCredentials(defaulttrue;adcCredentialSecretis then not required), andshareWithExporter(defaulttrue). If you enablevaultCredentialsand setupgradeImageAlwaystofalse,ingressController.imagemust be a NetScaler Ingress Controller 4.3.22 or later image, written with its version tag as<repository>:<tag>or<repository>:<tag>@sha256:<digest>. With an older image, or an image without a version tag (for example, only a digest,latest, or a build name), the operator does not deploy the controller and reportsVaultImageUnsupportedin the instance status. For more information, see Use NetScaler credentials stored in a Vault server.The following examples are complete NetscalerIngressController resources that show how to set some of these parameters. Update the values for your environment before you click Create.Example: Read the NetScaler credentials from HashiCorp Vault. A Vault Agent sidecar writes the NetScaler user name and password to thecitrix-credsvolume that the operator adds, soadcCredentialSecretis not needed. Set up Vault, thevault-agent-configConfigMap, and a Vault role for the service account of the instance (by default, the instance name) as described in Use NetScaler credentials stored in a Vault server.apiVersion: netscaler.com/v1
kind: NetscalerIngressController
metadata:
name: nsic-vault
spec:
acceptLicense: 'Yes'
ingressController:
entityPrefix: nsic
ingressClass:
- nsic-vpx
netscaler:
nsIP: 10.0.0.10
# No adcCredentialSecret: the Vault Agent sidecar supplies the credentials
vaultCredentials:
enabled: true
extraEnv:
# Optional: seconds between checks for new credentials (default 30)
- name: NS_CRED_RELOAD_INTERVAL
value: "60"
extraContainers:
- name: vault-agent
image: hashicorp/vault:<version>
args: ["agent", "-config=/etc/vault/vault-agent-config.hcl"]
env:
- name: VAULT_ADDR
value: "https://<vault-server>:8200"
# Needed when the container does not run as root, for example on OpenShift
- name: SKIP_SETCAP
value: "true"
volumeMounts:
# citrix-creds is the shared in-memory volume that the operator adds
- name: citrix-creds
mountPath: /etc/citrix
- name: vault-config
mountPath: /etc/vault
- name: vault-token
mountPath: /home/vault
- name: sa-token
mountPath: /var/run/secrets/kubernetes.io/serviceaccount
readOnly: true
extraVolumes:
- name: vault-config
configMap:
name: vault-agent-config
- name: vault-token
emptyDir:
medium: Memory
- name: sa-token
projected:
sources:
- serviceAccountToken:
path: token
expirationSeconds: 3600
audience: vault # the token works only for Vault, not for the Kubernetes APIIf you also enable the metrics exporter (exporter.required: true), add a Vault Agent init container underinitContainers: the same container as thevault-agentsidecar, with-exit-after-authadded toargs. The exporter reads the credential files only once, when it starts, so they must exist before it starts. Restart the pod after each credential rotation.Example: Validate the NetScaler certificate in the metrics exporter. To validate the certificate when you enable the exporter withoutingressController.nsValidateCert, setexporter.validateCert. Enclose the value in quotes so that YAML does not read values such asyesas Boolean values.apiVersion: netscaler.com/v1
kind: NetscalerIngressController
metadata:
name: nsic
spec:
acceptLicense: 'Yes'
ingressController:
entityPrefix: nsic
ingressClass:
- nsic-vpx
netscaler:
nsIP: 10.0.0.10
adcCredentialSecret: nslogin
exporter:
required: true
# "auto" validates against the trust store in the exporter image.
# Always quote this value, for example "yes" or "no".
validateCert: "auto"Example: Validate the NetScaler certificate against your CA. NetScaler Ingress Controller and the metrics exporter validate the NetScaler certificate against the CA in thenscacertsecret. You must also sethostAliases; otherwise, the operator does not deploy NetScaler Ingress Controller.apiVersion: netscaler.com/v1
kind: NetscalerIngressController
metadata:
name: nsic
spec:
acceptLicense: 'Yes'
ingressController:
entityPrefix: nsic
ingressClass:
- nsic-vpx
nsValidateCert:
# Secret that holds the NetScaler CA certificate under the key nsCA.pem
nsCertSecret: nscacert
# Required with nsValidateCert: maps nsIP to the host name in the NetScaler certificate
hostAliases:
- ip: 10.0.0.10
hostnames:
- netscaler.example.com
netscaler:
nsIP: 10.0.0.10
adcCredentialSecret: nslogin
exporter:
required: trueExample: Stop publishing the VIP in the status of LoadBalancer services. SetupdateServiceStatustofalse. To also remove, at startup, the status that NetScaler Ingress Controller published earlier, setclearStaleServiceStatustotrue. While both are set, the operator rolls out the pod with theRecreatestrategy.apiVersion: netscaler.com/v1
kind: NetscalerIngressController
metadata:
name: nsic
spec:
acceptLicense: 'Yes'
ingressController:
entityPrefix: nsic
ingressClass:
- nsic-vpx
# Do not publish the NetScaler VIP in the status of type LoadBalancer services.
updateServiceStatus: false
# Optional: at startup, remove the status that this controller published earlier.
clearStaleServiceStatus: true
netscaler:
nsIP: 10.0.0.10
adcCredentialSecret: nsloginExample: Configure routes only for selected nodes. WithnodeWatchset totrue, NetScaler Ingress Controller configures routes only for the nodes that have all the labels innodeWatchLabelSelector.apiVersion: netscaler.com/v1
kind: NetscalerIngressController
metadata:
name: nsic
spec:
acceptLicense: 'Yes'
ingressController:
entityPrefix: nsic
ingressClass:
- nsic-vpx
nodeWatch: true
# Configure routes only for the nodes that have all these labels.
nodeWatchLabelSelector:
topology.kubernetes.io/zone: zone-a
netscaler:
nsIP: 10.0.0.10
adcCredentialSecret: nslogin -
-
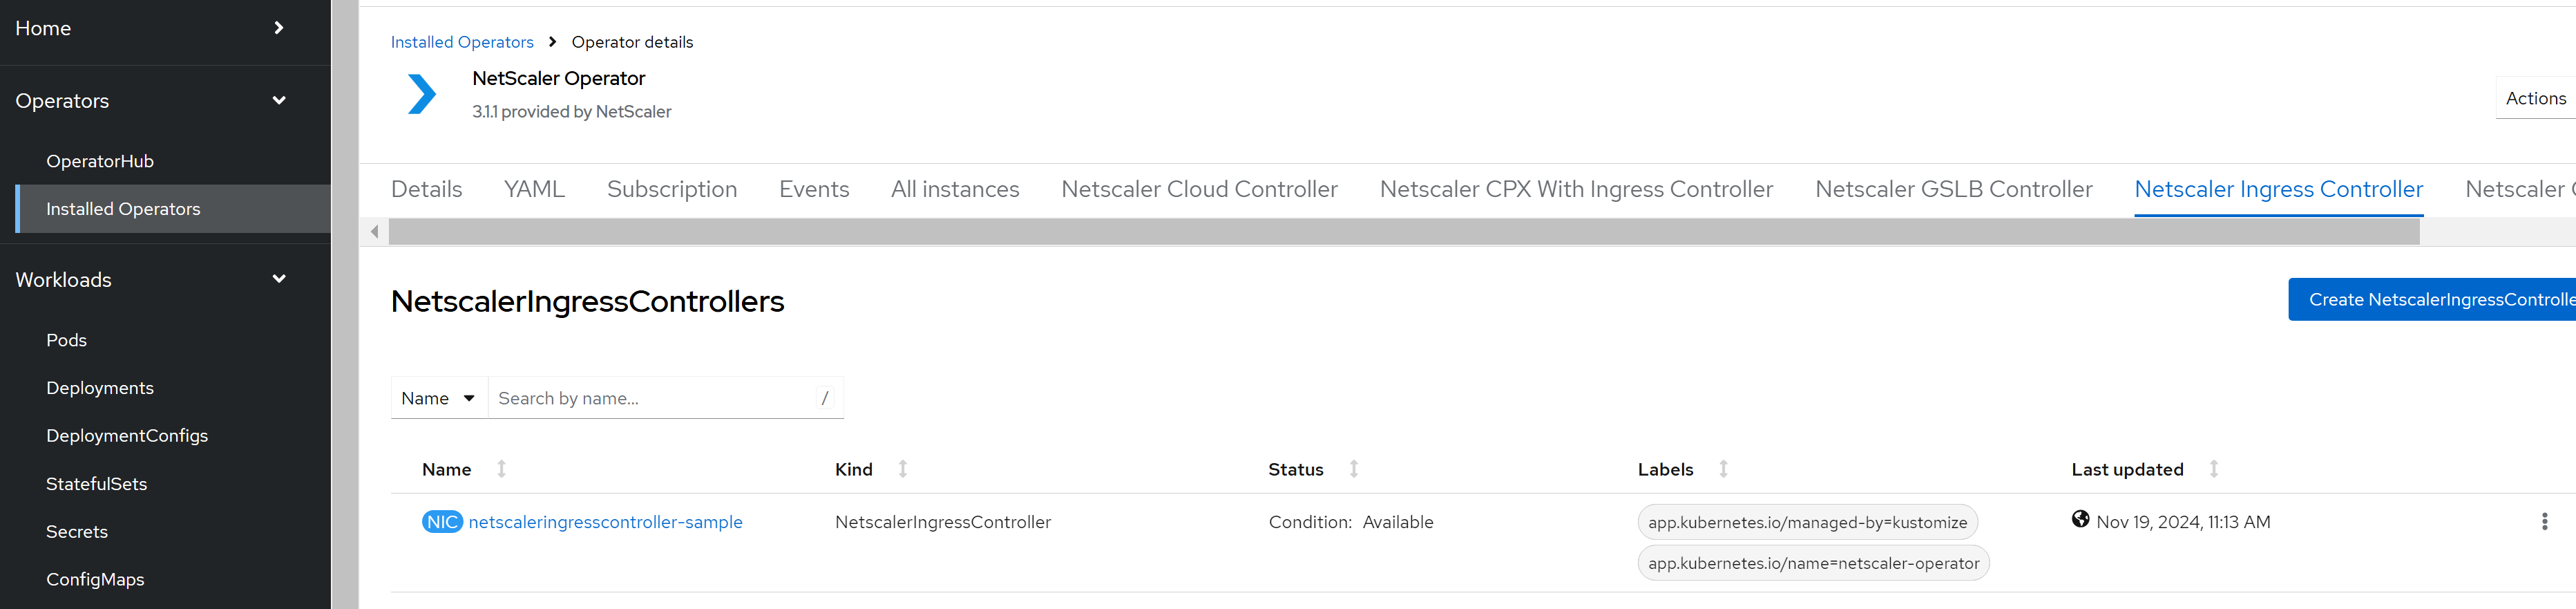
After updating the values for the required parameters, click Create.Ensure that NetScaler Ingress Controller is successfully deployed and initialized.
-
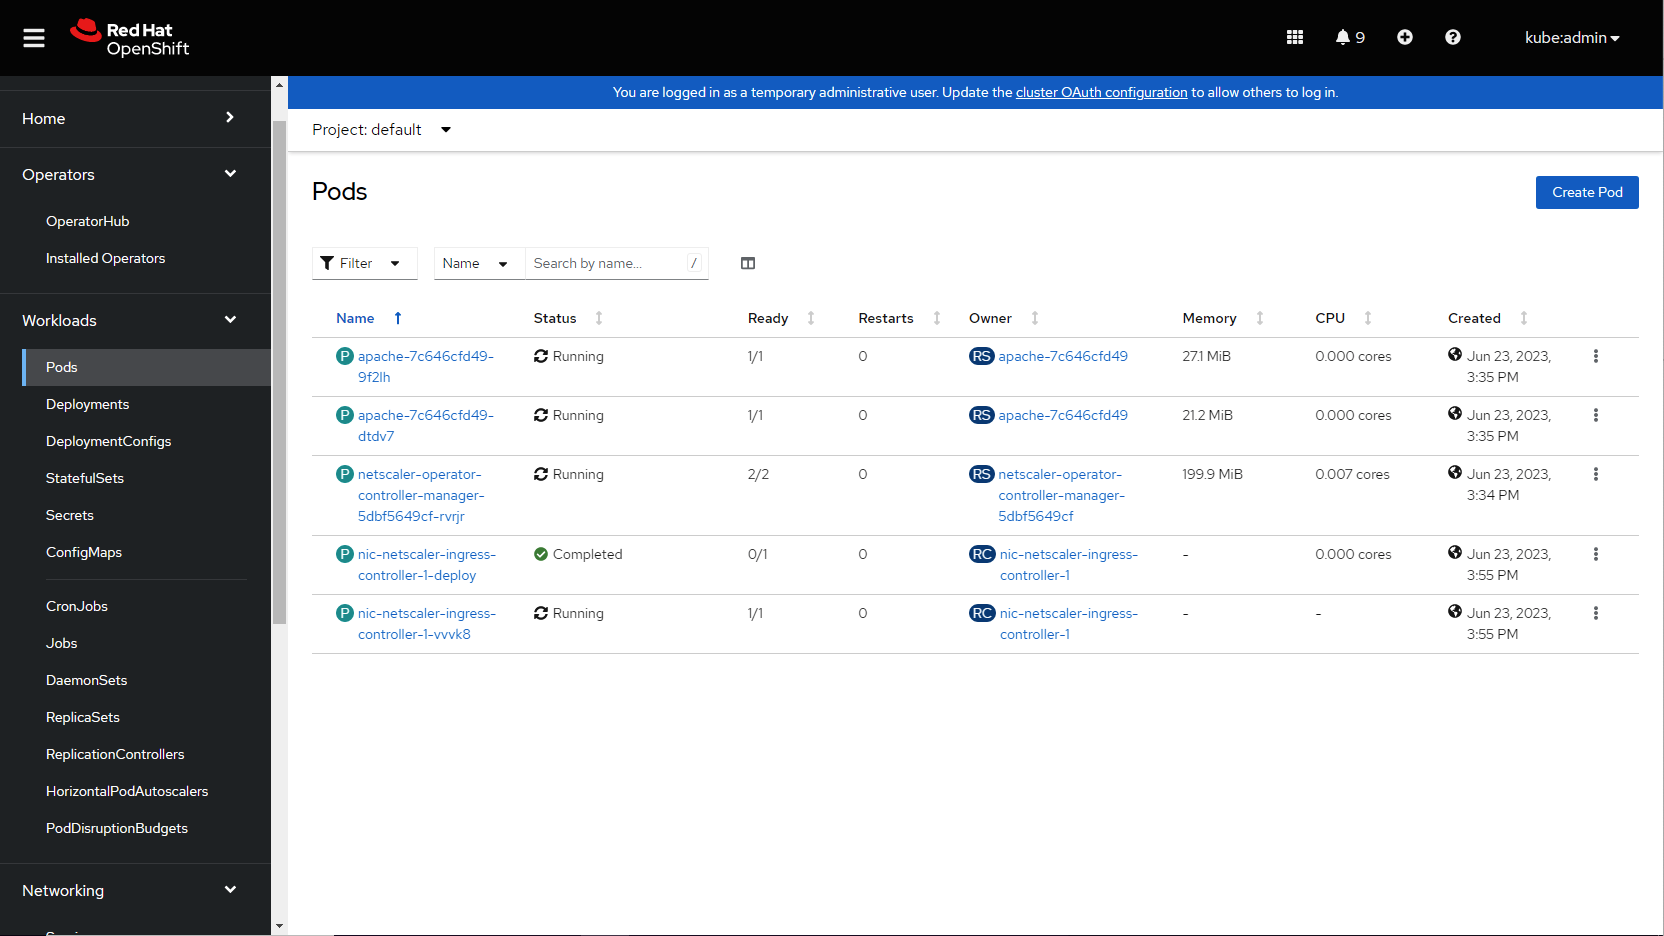
Navigate to Workloads > Pods section and verify whether the NetScaler Ingress Controller pod is up and running.
-
Verify the deployment by sending traffic:
curl http://citrix-ingress-Operator.com --resolve citrix-ingress-Operator.com:80:<VIP>The previous curl command should return the following:<html><body><h1>It works!</h1></body></html>
Note:
-
Ensure that the pod network in OpenShift cluster is reachable from NetScaler VPX or NetScaler MPX if you are using a service of type ClusterIP for your application. To configure static route automatically using NetScaler Ingress Controller, see Configure static route.
References
-
For information about how to deploy NetScaler Observability Exporter using NetScaler Operator, see Deploy NetScaler Observability Exporter using NetScaler Operator.
-
For information about how to deploy NetScaler Agent Operator, see Install a NetScaler agent operator using the OpenShift console.
-
Alternatively, you can deploy NetScaler Ingress Controller using Helm charts. See Deploy the NetScaler Ingress Controller using Helm charts.