
API gateway for Kubernetes
An API gateway acts as the single entry point for your APIs and ensures secure and reliable access to multiple APIs and microservices in your system.
NetScaler® provides an enterprise grade API gateway for North-South API traffic into the Kubernetes cluster. The API gateway integrates with Kubernetes through the NetScaler Ingress Controller and the NetScaler (NetScaler MPX, VPX, or CPX) deployed as the Ingress Gateway for on-premises or cloud deployments.
The following diagram shows a dual-tier topology for the API gateway.
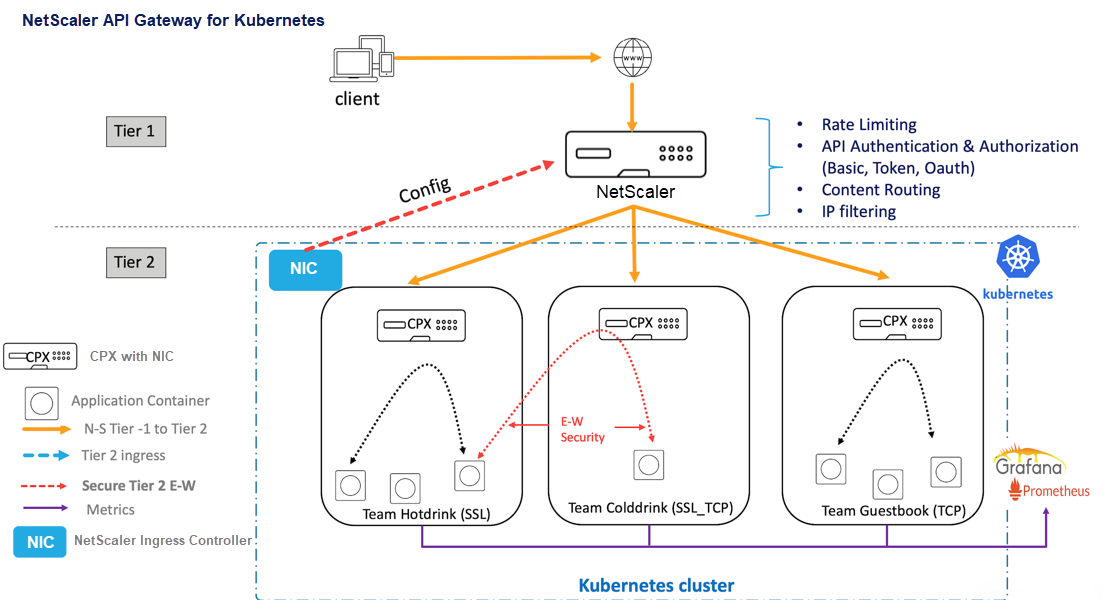
Using the API gateway offered by Citrix®, you can perform the following functionalities:
-
Enforce authentication policies
-
Rate limit access to services
-
Advanced content routing
-
Flexible and comprehensive transformation of HTTP transactions using the rewrite and responder policies
-
Enforce web application firewall policies
How does the API gateway work
The API gateway is built on top of the NetScaler Ingress Gateway and uses Kubernetes API extensions such as custom resource definitions (CRDs). Using CRDs, you can automatically configure the NetScaler and API gateway in the same instance.
NetScaler provides the following CRDs for the API gateway:
Key benefits of using the API gateway
Following are the key benefits of the API gateway offered by Citrix:
-
Uses the advanced traffic management and comprehensive security features of NetScaler.
-
Optimizes your deployments by consolidating multiple network functions into a single component of the NetScaler Ingress Gateway.
-
Reduces the operational complexity and cost involved in deploying multiple components.
-
Ensures better performance for your application traffic by reducing multiple hops of TCP or TLS decryption while using separate components.
-
Simplifies deploy and integrate in your Kubernetes environments either by directly using YAMLs or helm charts.
Deploying the API gateway
For more information on how to configure the API gateway features using CRDs, see the NetScaler Ingress Controller documentation: