-
Getting Started with NetScaler
-
Solutions for Telecom Service Providers
-
Load Balance Control-Plane Traffic that is based on Diameter, SIP, and SMPP Protocols
-
Provide Subscriber Load Distribution Using GSLB Across Core-Networks of a Telecom Service Provider
-
Authentication, authorization, and auditing application traffic
-
Basic components of authentication, authorization, and auditing configuration
-
Web Application Firewall protection for VPN virtual servers and authentication virtual servers
-
On-premises NetScaler Gateway as an identity provider to Citrix Cloud™
-
Authentication, authorization, and auditing configuration for commonly used protocols
-
Troubleshoot authentication and authorization related issues
-
Troubleshoot authentication, authorization and auditing issues
-
Configure EULA as an authentication factor in NetScaler nFactor system
-
Configure periodic Endpoint Analysis scan as a factor in nFactor authentication
-
Configure post-authentication Endpoint Analysis scan as a factor in NetScaler nFactor authentication
-
Configure pre-authentication Endpoint Analysis scan as a factor in nFactor authentication
-
Configure pre-auth and post-auth EPA scan as a factor in nFactor authentication
-
Configure prefill user name from certificate in NetScaler nFactor authentication
-
Localize error messages generated by NetScaler nFactor system
-
Configure NetScaler Gateway preauthentication EPA scan for the domain check
-
-
-
-
-
-
Persistence and persistent connections
-
Advanced load balancing settings
-
Gradually stepping up the load on a new service with virtual server–level slow start
-
Protect applications on protected servers against traffic surges
-
Retrieve location details from user IP address using geolocation database
-
Use source IP address of the client when connecting to the server
-
Use client source IP address for backend communication in a v4-v6 load balancing configuration
-
Set a limit on number of requests per connection to the server
-
Configure automatic state transition based on percentage health of bound services
-
-
Use case 2: Configure rule based persistence based on a name-value pair in a TCP byte stream
-
Use case 3: Configure load balancing in direct server return mode
-
Use case 6: Configure load balancing in DSR mode for IPv6 networks by using the TOS field
-
Use case 7: Configure load balancing in DSR mode by using IP Over IP
-
Use case 10: Load balancing of intrusion detection system servers
-
Use case 11: Isolating network traffic using listen policies
-
Use case 12: Configure Citrix Virtual Desktops for load balancing
-
Use case 13: Configure Citrix Virtual Apps and Desktops for load balancing
-
Use case 14: ShareFile wizard for load balancing Citrix ShareFile
-
Use case 15: Configure layer 4 load balancing on the NetScaler appliance
-
-
-
-
Create a certificate signing request and use SSL certificates on a NetScaler appliance
-
Configure SSL acceleration with HTTP on the front end and SSL on the back end
-
Export certificates used on a NetScaler appliance as PFX file
-
Configure SSL monitoring when client authentication is enabled on the back-end service
-
Configure SSL action to forward client traffic if a cipher is not supported on the ADC
-
Configure synchronization of files in a high availability setup
-
-
-
Authentication and authorization for System Users
-
-
Configuring a CloudBridge Connector Tunnel between two Datacenters
-
Configuring CloudBridge Connector between Datacenter and AWS Cloud
-
Configuring a CloudBridge Connector Tunnel Between a Datacenter and Azure Cloud
-
Configuring CloudBridge Connector Tunnel between Datacenter and SoftLayer Enterprise Cloud
-
Configuring a CloudBridge Connector Tunnel Between a NetScaler Appliance and Cisco IOS Device
-
CloudBridge Connector Tunnel Diagnostics and Troubleshooting
This content has been machine translated dynamically.
Dieser Inhalt ist eine maschinelle Übersetzung, die dynamisch erstellt wurde. (Haftungsausschluss)
Cet article a été traduit automatiquement de manière dynamique. (Clause de non responsabilité)
Este artículo lo ha traducido una máquina de forma dinámica. (Aviso legal)
此内容已经过机器动态翻译。 放弃
このコンテンツは動的に機械翻訳されています。免責事項
이 콘텐츠는 동적으로 기계 번역되었습니다. 책임 부인
Este texto foi traduzido automaticamente. (Aviso legal)
Questo contenuto è stato tradotto dinamicamente con traduzione automatica.(Esclusione di responsabilità))
This article has been machine translated.
Dieser Artikel wurde maschinell übersetzt. (Haftungsausschluss)
Ce article a été traduit automatiquement. (Clause de non responsabilité)
Este artículo ha sido traducido automáticamente. (Aviso legal)
この記事は機械翻訳されています.免責事項
이 기사는 기계 번역되었습니다.책임 부인
Este artigo foi traduzido automaticamente.(Aviso legal)
这篇文章已经过机器翻译.放弃
Questo articolo è stato tradotto automaticamente.(Esclusione di responsabilità))
Translation failed!
Configure SAML single sign-on
To provide single sign-on capabilities across applications that are hosted on the service provider, you can configure SAML single sign-on on the SAML SP.
Configuring SAML single sign-on by using the CLI
-
Configure the SAML SSO profile.
Example
In the following command, Example is the load balancing virtual server that has a web link from the SharePoint portal. Nssp.example.com is the Traffic Management virtual server that is load balancing the SharePoint server.
add tm samlSSOProfile tm-saml-sso -samlSigningCertName nssp -assertionConsumerServiceURL "https://nssp2.example.com/cgi/samlauth" -relaystateRule "\\"https://nssp2.example.com/samlsso.html\\"" -sendPassword ON -samlIssuerName nssp.example.com <!--NeedCopy--> -
Associate the SAML SSO profile with the traffic action.
Example
The following command enables SSO and binds the SAML SSO profile created above to a traffic action.
add tm trafficAction html_act -SSO ON -samlSSOProfile tm-saml-sso <!--NeedCopy--> -
Configure the traffic policy that specifies when the action must be run.
Example
The following command associates the traffic action with a traffic policy.
add tm trafficPolicy html_pol "HTTP.REQ.URL.CONTAINS(\\"abc.html\\")" html_act <!--NeedCopy--> -
Bind the traffic policy created previously to a traffic management virtual server (load balancing or content switching). Alternatively, the traffic policy can be associated globally.
Note:
-
This traffic management virtual server must be associated with the relevant authentication virtual server that is associated with the SAML action.
-
In an nFactor setup, an authentication virtual server, which is redirected by a load balancer, cannot act as the identity provider for the back-end application.
bind lb vserver lb1_ssl -policyName html_pol -priority 100 -gotoPriorityExpression END -type REQUEST <!--NeedCopy--> -
Configuring SAML single sign-on by using the GUI
To configure SAML single sign-on you need to define the SAML SSO profile, the traffic profile, and the traffic policy and bind the traffic policy to a traffic management virtual server or globally to the NetScaler appliance.
-
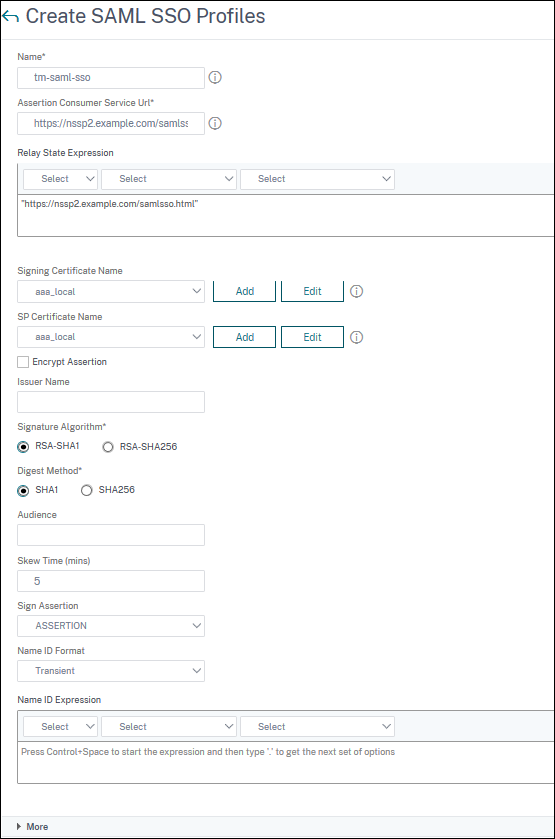
Navigate to Security > AAA-Application Traffic > Policies > Traffic > SAML SSO Profiles and click Add.
-
On the Create SAML SSO Profiles page, enter the values for the following fields and click Create.
-
Name: Name for the SAML SSO profile.
-
Assertion Consumer Service Url: URL to which the assertion must be sent.
-
Signing Certificate Name: Name of the SSL certificate that is used to sign assertion.
-
SP Certificate Name: Name of the SSL certificate of a peer or receiving party using which the assertion is encrypted.
-
Issuer Name: The name to be used in requests sent from NetScaler to IdP to uniquely identify NetScaler.
-
Signature Algorithm: Algorithm to be used to sign or verify SAML transactions.
-
Digest Method: Algorithm to be used to compute or verify digest for SAML transactions.
-
Audience: Audience for which an assertion sent by IdP is applicable. This is typically an entity name or url that represents a service provider.
-
Skew Time (mins): The number of minutes on either side of the current time that the assertion is valid.
-
Sign Assertion: Option to sign portions of assertion when NetScaler IdP sends one. Based on the user selection, either ASSERTION or RESPONSE or BOTH or NONE can be signed.
-
Name ID Format: Format of NameIdentifier sent in assertion.
-
Name ID Expression: Expression that is evaluated to obtain NameIdentifier to be sent in assertion.
-
-
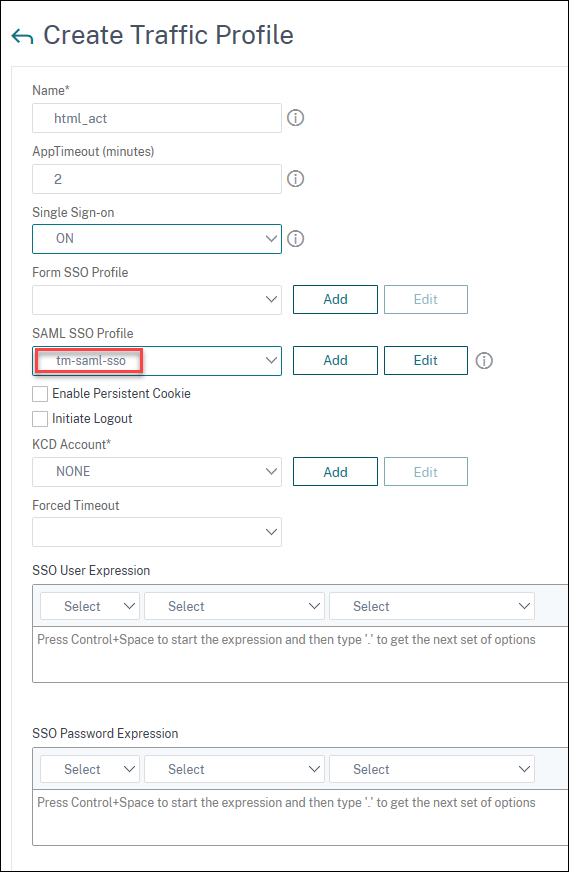
Navigate to Security > AAA-Application Traffic > Policies > Traffic > Traffic Profiles and click Add.
-
On the Create Traffic Profile page, enter the values for the following fields, and click Create.
-
Name: Name for the traffic action.
-
AppTimeout (minutes): Time interval, in minutes, of user inactivity after which the connection is closed.
-
Single Sign-on: Select ON.
-
SAML SSO Profile: Select the created SAML SSO profile.
-
KCD Account: Kerberos constrained delegation account name.
-
SSO User Expression: Expression that is evaluated to obtain user name for SingleSignOn.
-
SSO Password Expression: Expression that is evaluated to obtain password for SingleSignOn
-
-
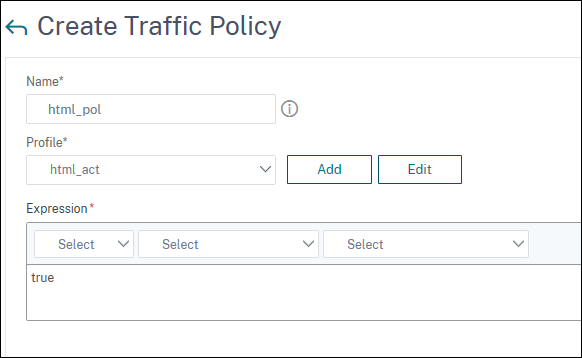
Navigate to Security > AAA-Application Traffic > Policies > Traffic > Traffic Policies and click Add.
-
On the Create Traffic policy page, enter the values for the following, and click Create.
-
Name: Name of the traffic policy to be created.
-
Profile: Select the created traffic profile.
-
Expression: Advanced policy expression that the policy uses to respond to specific request. For example, true.
-
-
To bind the traffic policy to a traffic management virtual server, navigate to Traffic Management > Load Balancing > Virtual Servers, select a virtual server, and click Edit.
-
Under Advanced Settings, click Policies.
-
Select Traffic in the Choose Policy field, select Request in the Choose Type field, and click Continue.
-
Under Select Policy, click to select the created traffic.
-
Click Select.
-
Click Bind to bind the traffic policy to the virtual server.
Share
Share
This Preview product documentation is Cloud Software Group Confidential.
You agree to hold this documentation confidential pursuant to the terms of your Cloud Software Group Beta/Tech Preview Agreement.
The development, release and timing of any features or functionality described in the Preview documentation remains at our sole discretion and are subject to change without notice or consultation.
The documentation is for informational purposes only and is not a commitment, promise or legal obligation to deliver any material, code or functionality and should not be relied upon in making Cloud Software Group product purchase decisions.
If you do not agree, select I DO NOT AGREE to exit.